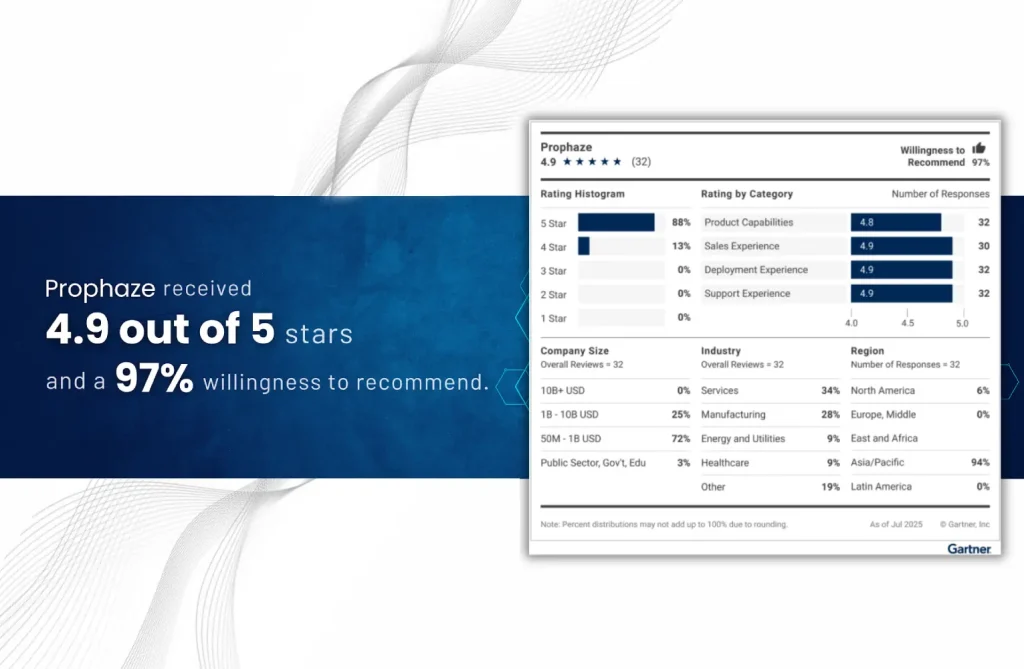
Resources Latest Resources Recognized as a Strong Performer in Gartner Peer Insights™ “Voice of the Customer” 2025 for Cloud Web Application and API Protection Learn More All Blog Case Studies Press Release Reports Datasheets Webinars All Blog Case Studies Press Release Reports Datasheets Webinars Blog AI Security Strategy: How to Build a Framework for Securing Enterprise AI Key Takeaways AI security spans models, agents, data, identities, and third-party integrations – not just Read More September 18, 2026 Blog API Gateway Security: Risks, Best Practices and How WAAP Closes the Gaps Key Takeaways API gateway security is the set of controls, mainly authentication, authorization, and rate Read More September 17, 2026 Blog Weekly Threat Report September 9–16, 2026: GitLab API File Read, Cisco ISE Bypass, WSO2 JWT Forgery & Issabel PBX RCE Reporting Convention New this week refers to vulnerabilities, exploits, or incidents disclosed between September 9–16. Read More September 17, 2026 Blog The Attack Surface Is Growing. Here’s What the AI Security Threat Report Reveals Two decades ago, security meant building a wall. Today, the wall is gone. Every AI Read More September 17, 2026 Blog WAF for Government Agencies: 9 Compliance-Ready Features to Protect Citizen Data Key Takeaways Government WAF procurement for compliance spans two layers: federal (FedRAMP, FISMA, NIST 800-53) Read More September 15, 2026 Blog AI Security Market Trends: Why Securing AI Is Becoming a New Security Category Key Takeaways Analyst estimates put the AI-in-cybersecurity market anywhere from $25B to $36B in 2026, Read More September 14, 2026 Blog WAF Virtual Patching: How Security Teams Buy Time Between Disclosure and Fix About Prophaze Technologies The median time to exploit a new vulnerability is now under 5 Read More September 11, 2026 Blog GraphQL API Security Solution: What Enterprises Need to Stop the Fastest-Growing API Attack Vector About Prophaze Technologies GraphQL APIs now carry more of the enterprise attack surface than the Read More September 11, 2026 Blog API Security for Small Business: Enterprise-Grade Protection That Fits Your Team Key Takeaways Small businesses need API security: 46% of all data breaches hit companies with Read More September 10, 2026 Blog Weekly Threat Report September 1-8, 2026: Magento RCE, Exploited Langflow and Rails Flaws, N-central RMM Risk & the AI/API KEV Surge The Week in One Line An actively exploited, unauthenticated CVSS 10.0 Magento/Adobe Commerce RCE forced Read More September 9, 2026 Blog Post-Quantum API Security: Why Enterprises Need to Start Preparing Now Your encrypted API traffic may be unreadable today.That doesn’t mean it will stay that way.“Harvest Read More September 7, 2026 Blog Weekly Threat Report August 24–31, 2026: GitLab GraphQL Exploits, Adobe SSRF→ RCE, PaperCut Zero-Days & Kaltura’s Unpatched RCE The Week in One Line A critical GitLab GraphQL code-injection flaw moved from disclosure to Read More September 2, 2026 No posts found 1 2 3 … 12