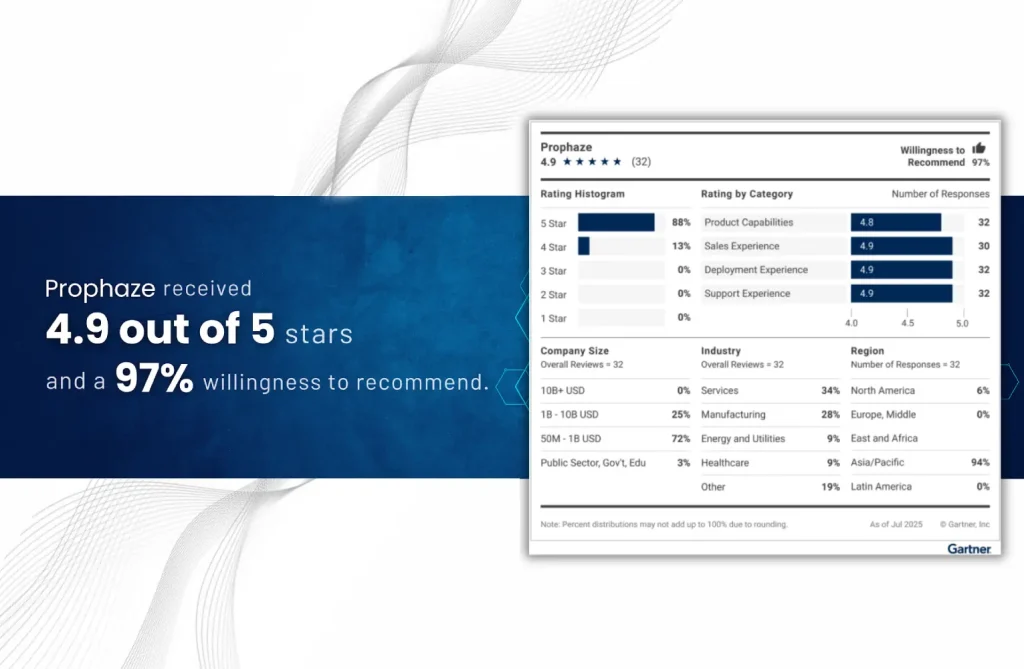
Blogs Latest Blog Recognized as a Strong Performer in Gartner Peer Insights™ “Voice of the Customer” 2025 for Cloud Web Application and API Protection Learn More All Blog Case Studies Press Release Reports Datasheets Webinars All Blog Case Studies Press Release Reports Datasheets Webinars Blog AI Security in Banking: Protecting Customer Data, LLMs, and AI Applications Key Takeaways AI security in banking is different from general AI security because model outputs Read More October 9, 2026 Blog How Do AI Security Guardrails Protect RAG Pipelines? Key Takeaways AI security guardrails are runtime controls between users, applications and LLMs. They work Read More October 9, 2026 Blog Weekly Threat Report September 30–October 6, 2026: Citrix NetScaler Zero-Days, FortiMail and Cisco SD-WAN Exploitation The Week in Short This week was dominated by internet-facing control-plane flaws: three actively exploited Read More October 8, 2026 Blog Fintech API Security Platform: Stop Breaches Hidden Inside Valid Payment Requests Key Takeaways Authentication-based attacks made up 92.4% of threats against banking and financial services in Read More October 7, 2026 Blog 7 Best Practices to Reduce WAF False Positives Without Losing Protection Key Takeaways A false positive is a legitimate request your WAF mistakenly blocks, and fixing Read More October 6, 2026 Blog Generative AI Security: How to Protect AI Applications from Prompt Injection, Data Leakage, and AI Attacks Key Takeaways Check Point’s AI Security Report 2026 found high-risk GenAI prompts, ones sharing sensitive Read More October 1, 2026 Blog Weekly Threat Report September 23–29, 2026: Citrix NetScaler RCE, F5 BIG-IP APM OAuth RCE, Next.js ImageResponse RCE, Cloudflare Containers Isolation, and AI-Agent Access Risk This week, the main focus was on vulnerabilities affecting internet-facing applications and identity infrastructure. There Read More September 30, 2026 Blog WAAP for Cybersecurity Mesh Architecture: One Policy Across Kubernetes, Cloud and On-Prem Apps Key Takeaways Cybersecurity mesh architecture (CSMA) replaces one network perimeter with security controls placed at Read More September 30, 2026 Blog AI Security in Financial Services: Risks, Threats, and How to Secure AI Systems Key Takeaways FinCEN’s November 2024 alert (FIN-2024-Alert004) confirmed a rise in deepfake-enabled fraud against financial Read More September 28, 2026 Blog CI/CD Pipeline Security: Protect Every App and API You Release Without Slowing Your Pipeline Key Takeaways CI/CD pipeline security covers two layers: the pipeline itself (code, secrets, dependencies, runners) Read More September 28, 2026 Blog Account Takeover Attack Prevention: The Attack Surface Most Security Teams Miss Key Takeaways Most account takeover attack prevention programs are built around credential stuffing and stop Read More September 24, 2026 Blog Weekly Threat Report September 17–22, 2026: Brevo Cloudflare Key Compromise, Escalating Orkes Workflow RCE, WordPress Comment2Shell & Bifrost AI Gateway Risk The Week in One Line A compromised Cloudflare API key enabled attackers to tamper with Read More September 23, 2026 No posts found 1 2 3 … 12