Web Attacks Are Evolving Fast. Prophaze WAF Security Platform Stops Them at the First Request.

Full lifecycle, AI driven WAF protection for cloud, Kubernetes, hybrid, and on prem applications. Predict, detect, and block zero-day attacks, bots, and Layer 7 DDoS with adaptive machine learning that safeguards every request without impacting performance or DevOps velocity.

Web Attack Surface Is Expanding
Faster Than Security

Web applications are no longer static websites. They are API driven, cloud connected, constantly changing systems running 24/7. Before you can defend web applications, you need visibility into how they are being targeted. Static, rule based WAFs struggle with evolving attack techniques, encrypted traffic, and automated abuse. Prophaze WAF continuously analyzes live traffic patterns to detect and stop threats that bypass legacy controls.

Signature based WAFs fail against zero day exploits.

High false positives disrupt real users.

Bots imitate real users and evade static rules.

Fragmented protection across cloud, Kubernetes, and on-prem.

A Unified WAF Platform Designed for
Modern Web Architectures

Prophaze WAF combines AI, deep traffic inspection, and adaptive learning to protect applications at scale without slowing performance or developers.

AI-powered threat detection that adapts in real time
Zero-day attack prevention before signatures exist
Bot mitigation for scraping, credential stuffing, and abuse
Layer 7 DDoS protection using behavioral rate controls, bundled rather than sold as an add-on
Fine-grained policy enforcement per application, managed as policy-as-code
Compliance-ready security aligned with OWASP, PCI-DSS, and HIPAA
How Prophaze WAF Engine Protects APP in Real-Time

Prophaze WAF inspects traffic inline or at the edge using AI driven analytics to distinguish legitimate users from attackers without interrupting normal application behavior.

Traffic Ingestion

Captures HTTP/HTTPS traffic with no code changes

Behavioral Analysis

Builds baselines for normal user and bot behavior

Real-Time Mitigation

Blocks, challenges, or rate-limits malicious traffic

Prophaze
Hybrid WAF

Deep Inspection

Headers, parameters, cookies, payloads

Anomaly Detection

Unusual request patterns

Continuous Learning

Models evolve as traffic changes

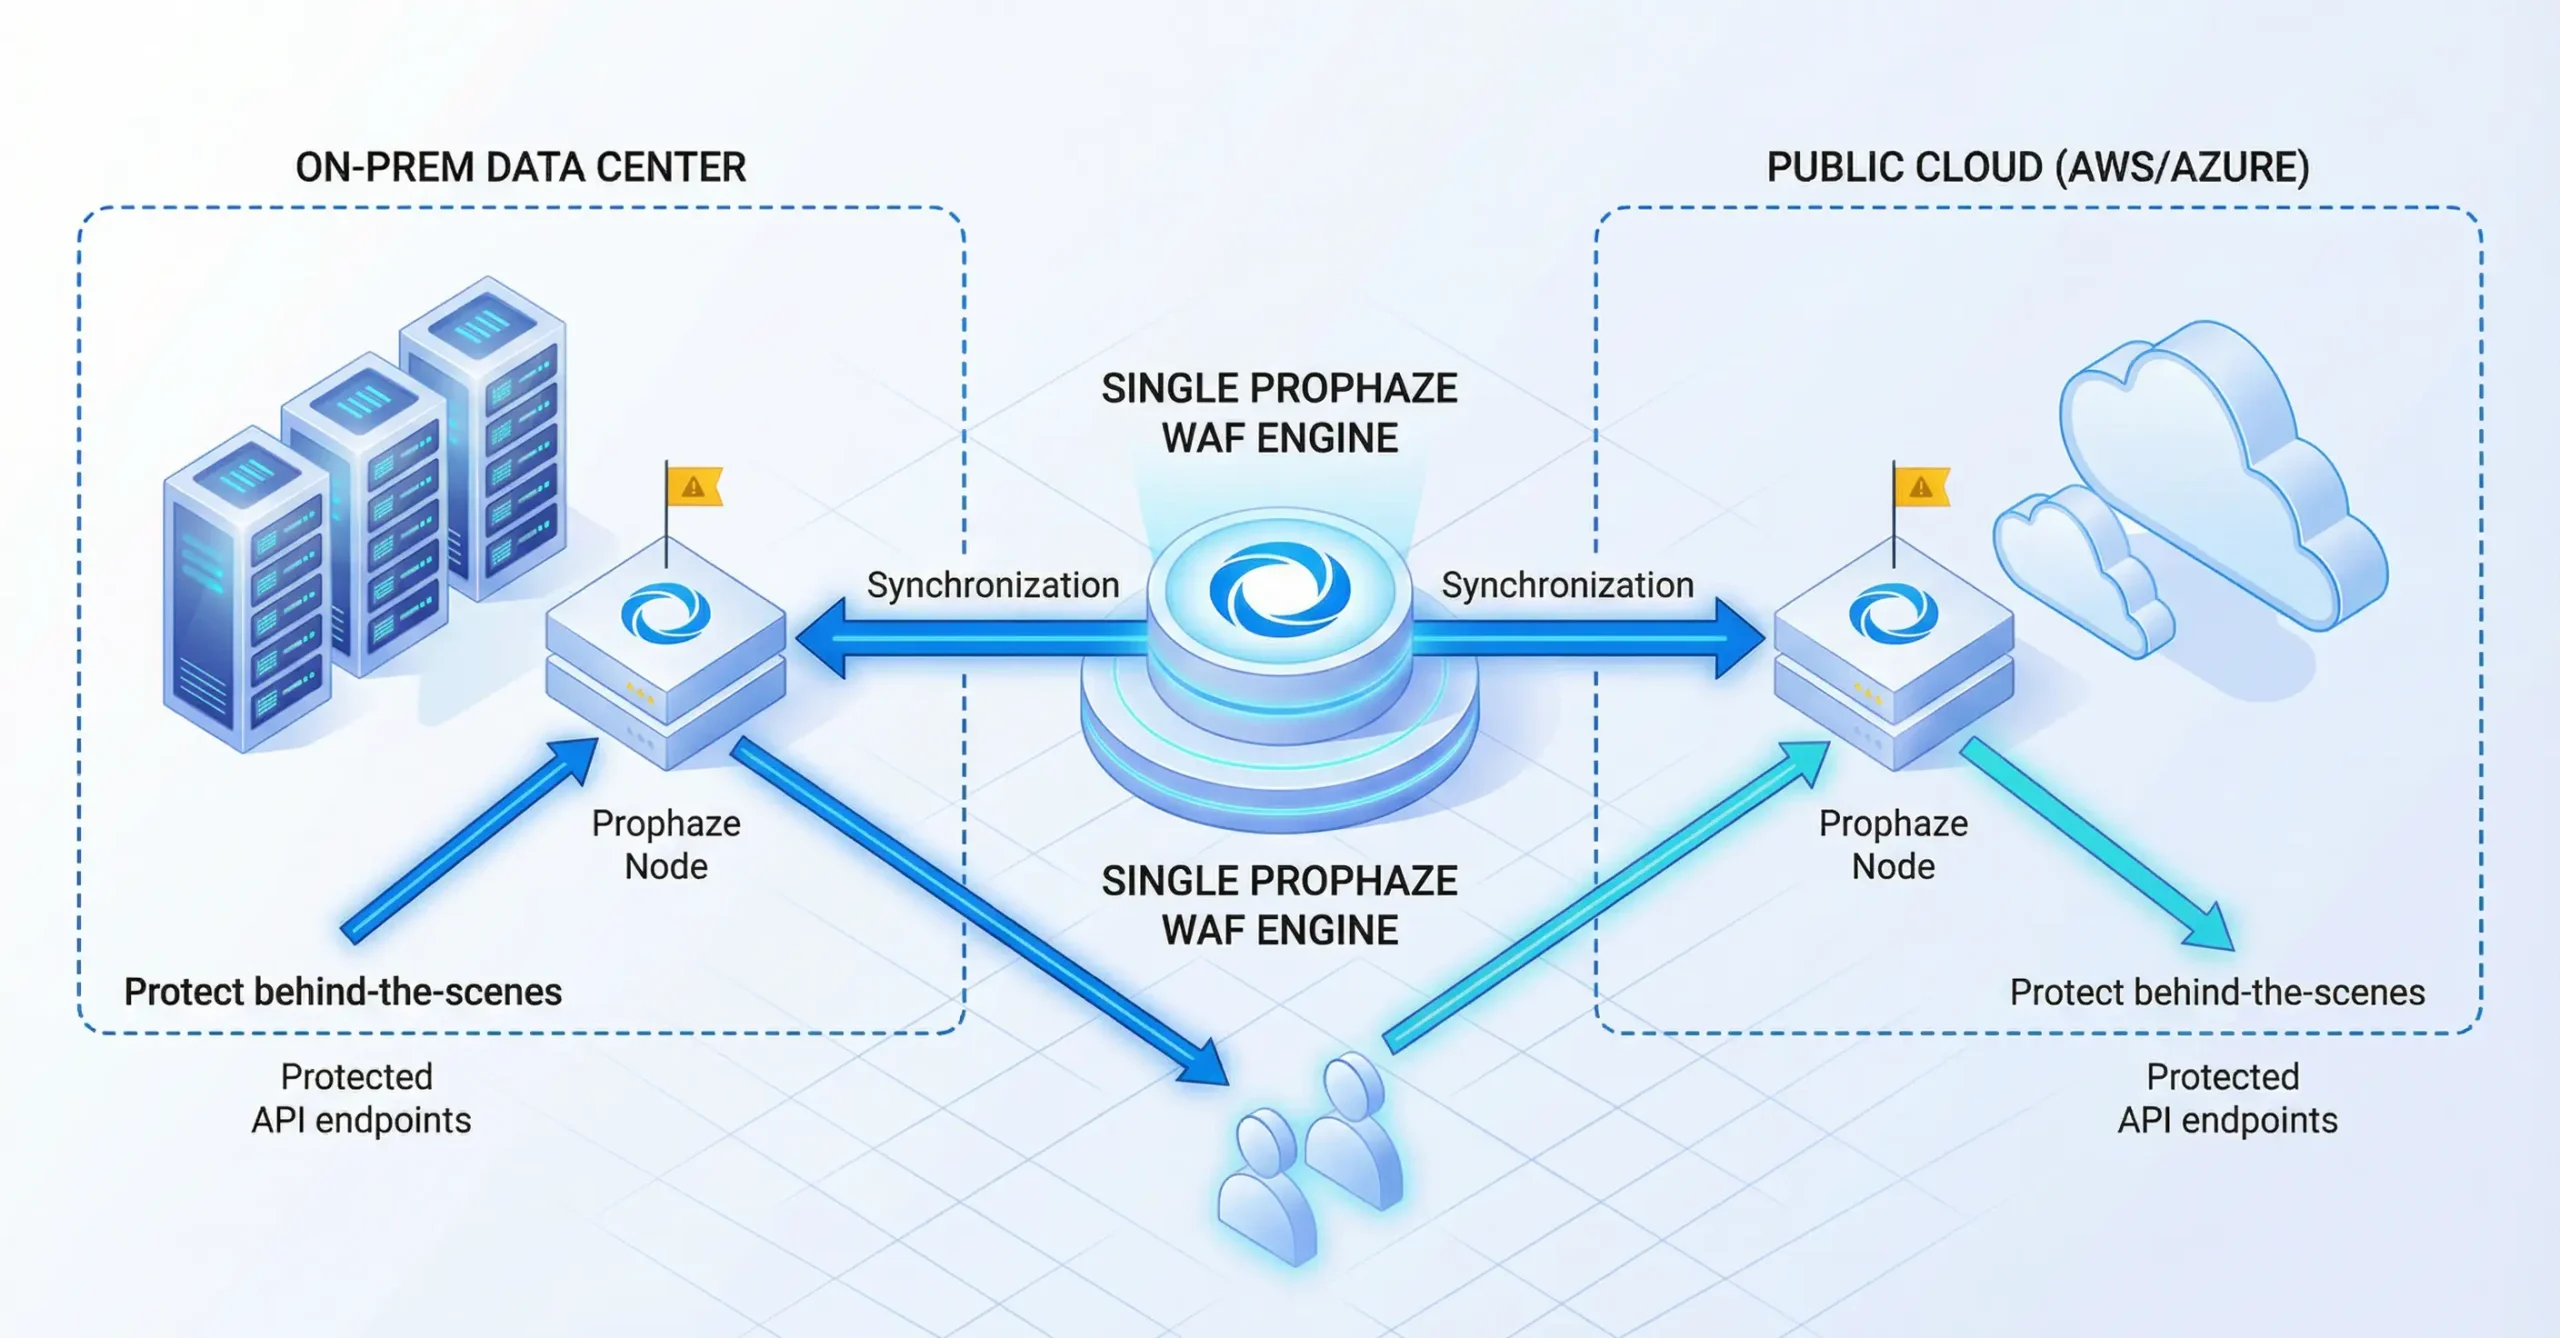
Flexible Deployment Models Powered by a Single WAF Engine

Prophaze WAF adapts to your infrastructure, not the other way around, ensuring consistent security across all environments. Choosing between cloud and hybrid WAF deployment depends on your compliance requirements and existing infrastructure. Prophaze supports all four deployment models from a single control plane.

From First Request to Full Control —in Three Moves

Observe and understand application behavior

Identify threats with context

Enforce consistent policies everywhere

Healthcare Deflecting 250 Million Application & API Attacks on Healthcare Systems with Prophaze WAAP

Kerala’s healthcare ecosystem has rapidly evolved into a digitally driven infrastructure supporting patient records, appointment systems, diagnostics, and real-time clinical workflows.

DevSecOps Fighting False Positives,
Prophaze Delivers Frictionless WAF Control

Prophaze WAF fits into CI/CD pipelines and container orchestrations without SDKs or code changes, giving security teams real-time threat blocking across monoliths, microservices, and Kubernetes while DevOps ships faster and auditors stay happy.

Proxy less deployment, zero app rewrites
Policy as code for GitOps and IaC workflows
Native Kubernetes and multi-cloud support with CDN integration
Granular RBAC with full audit compliance
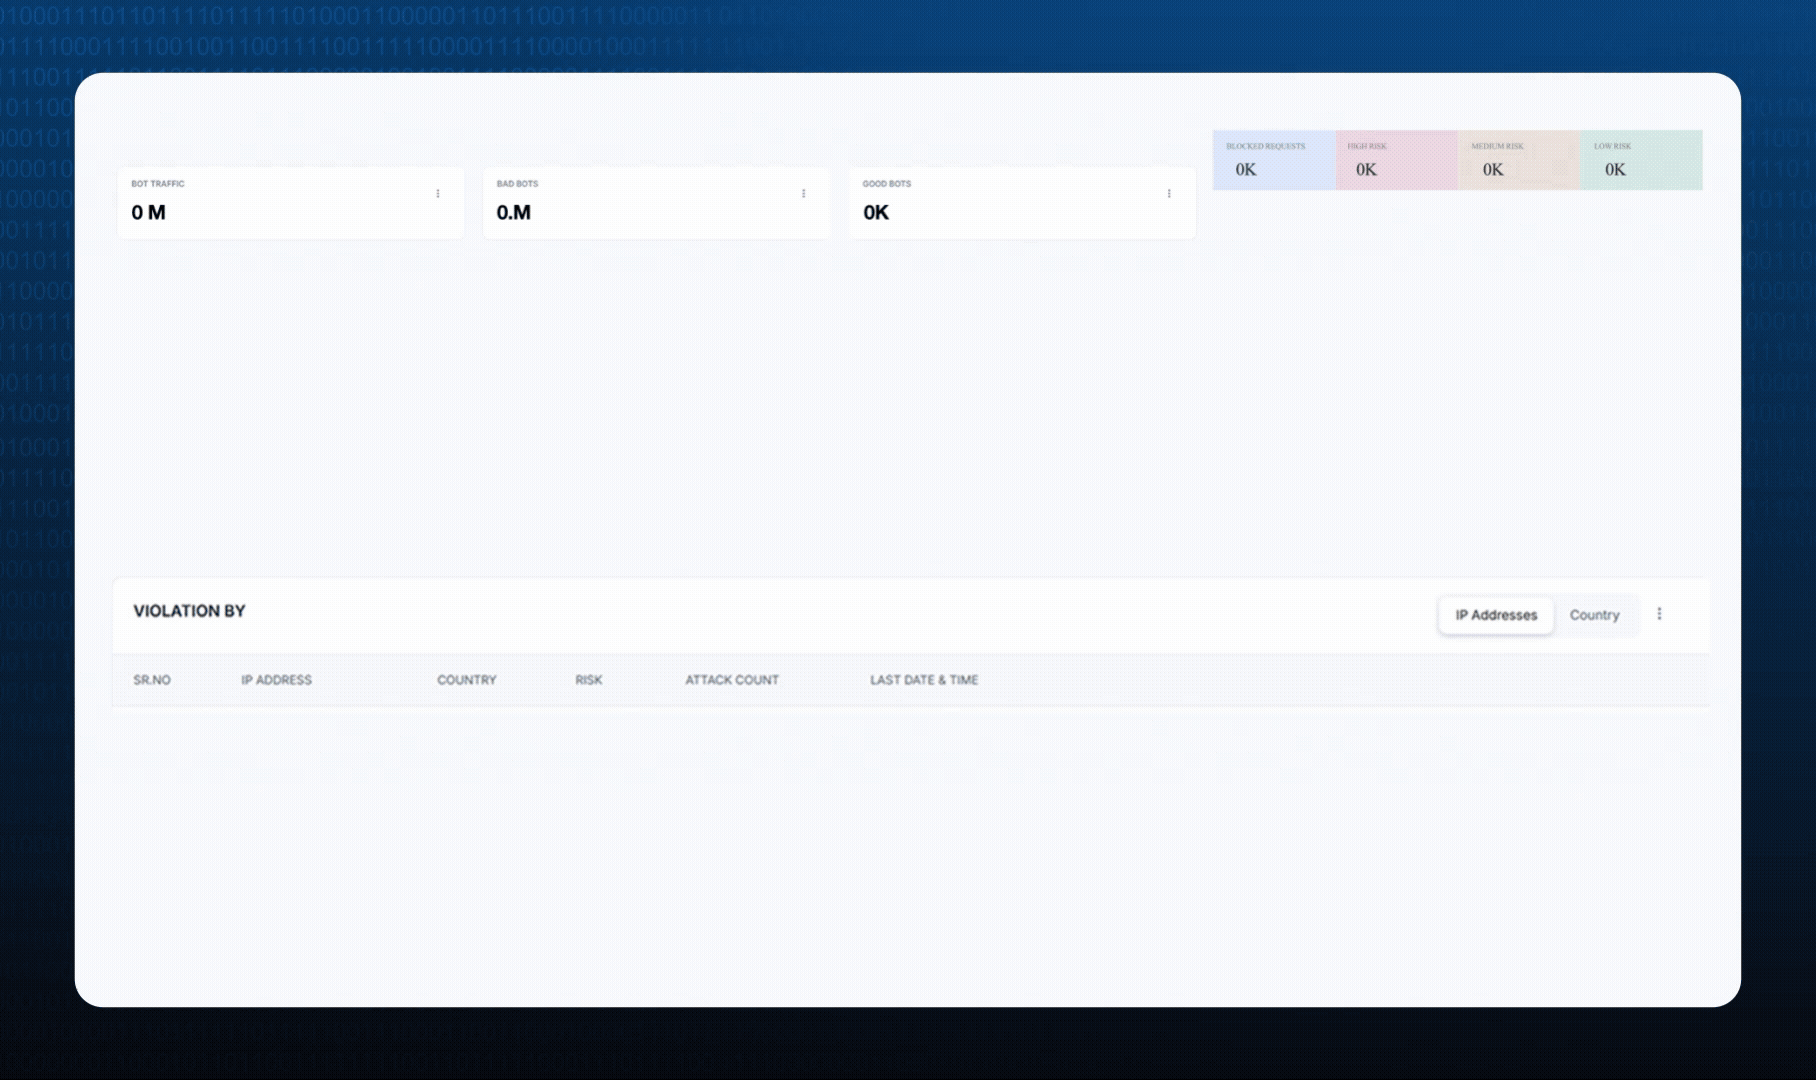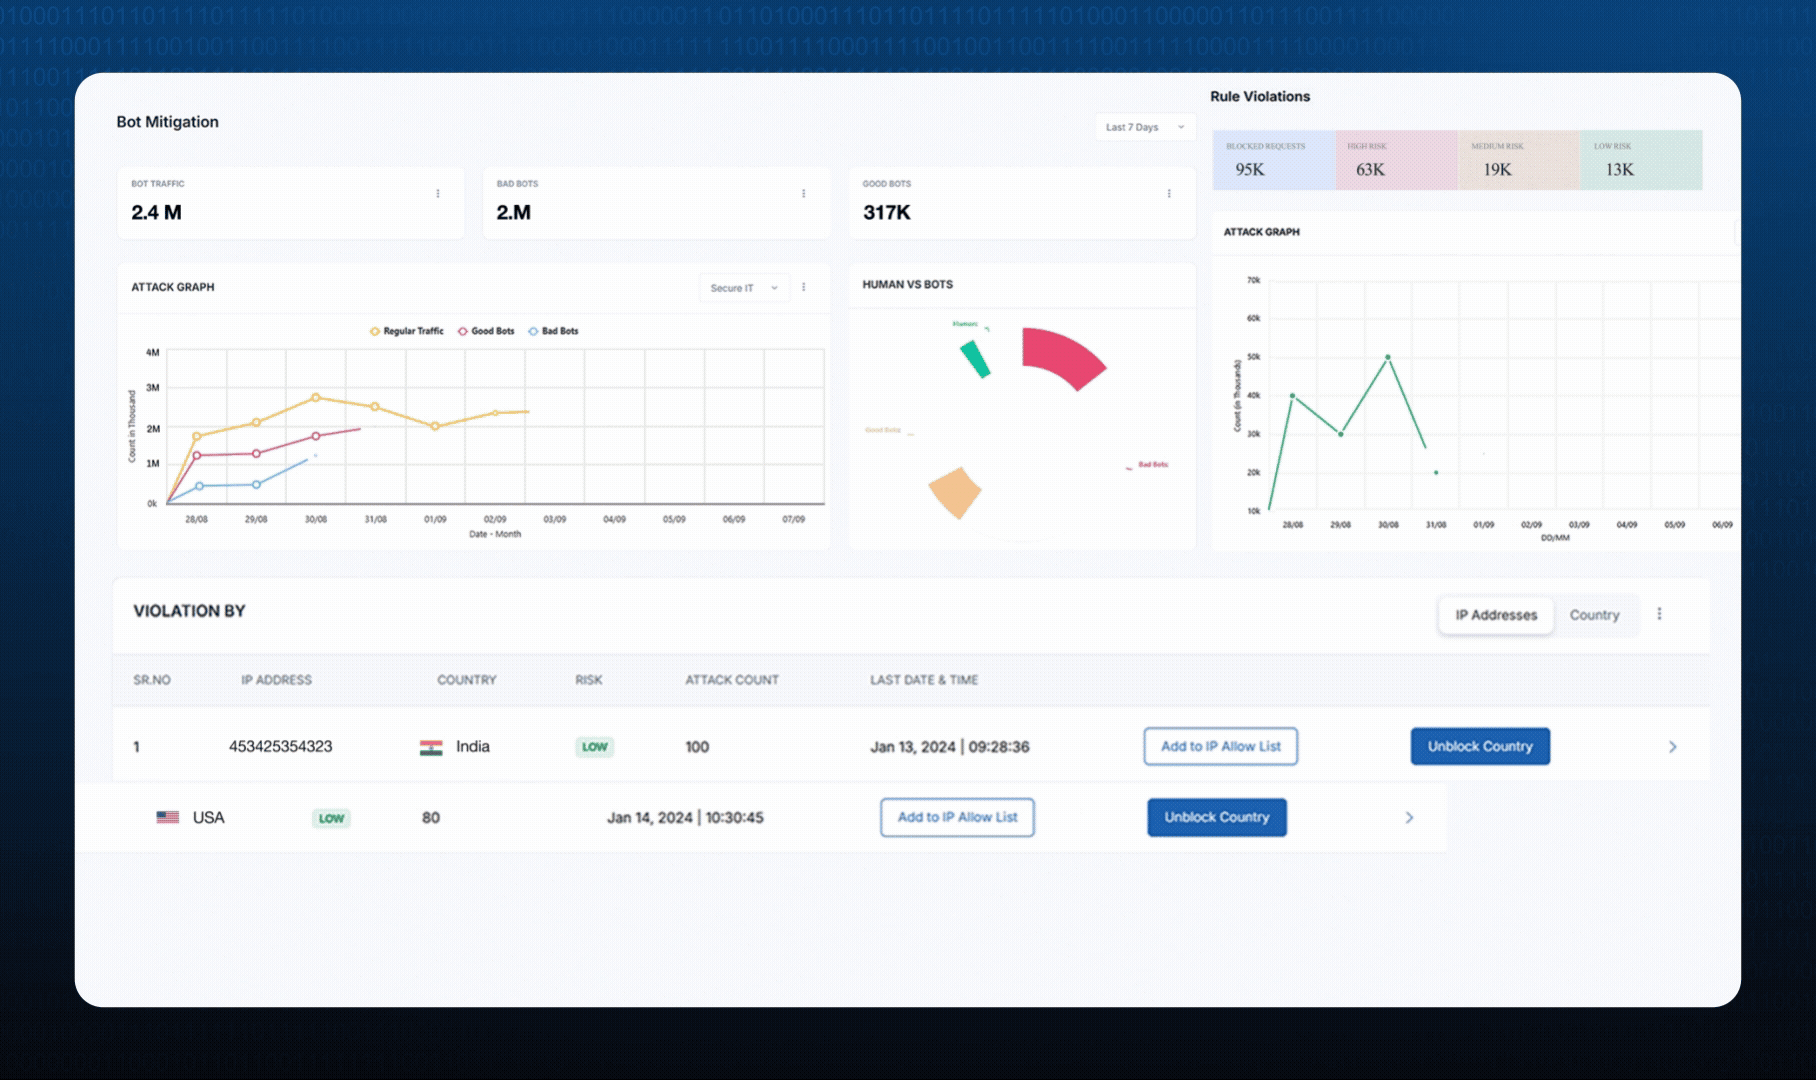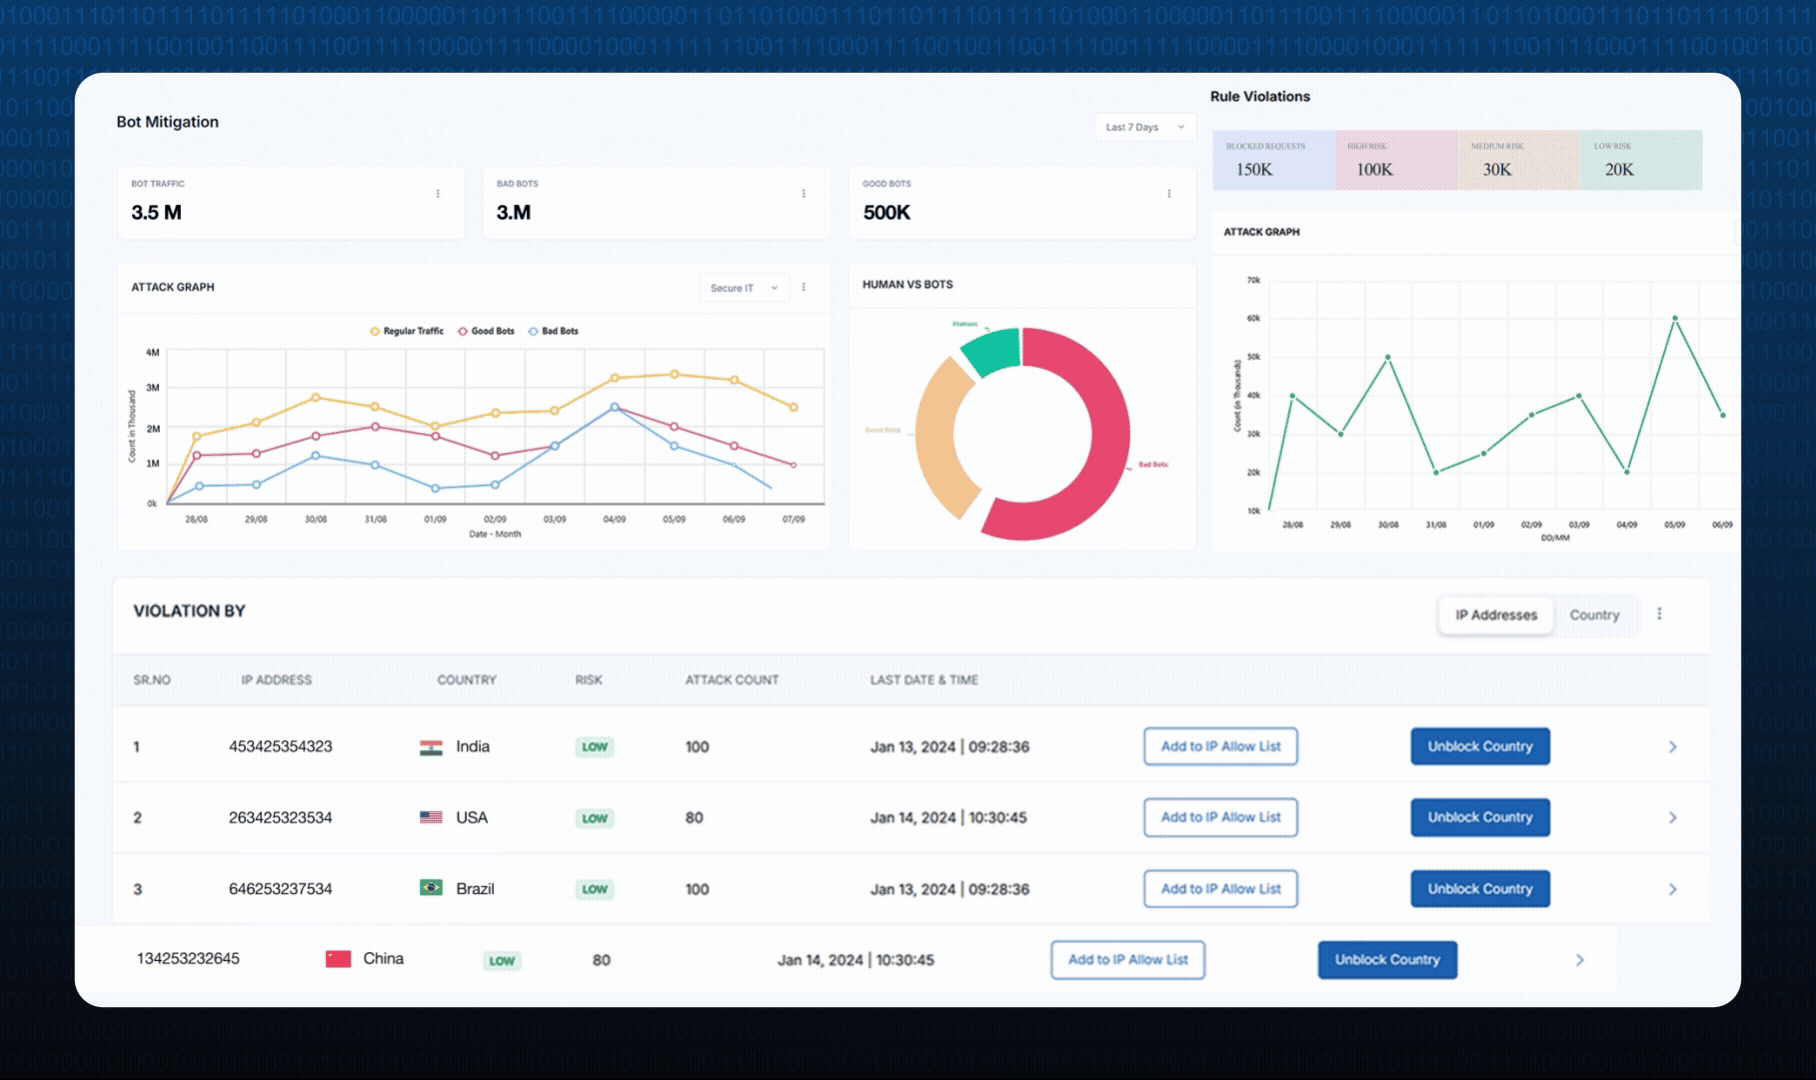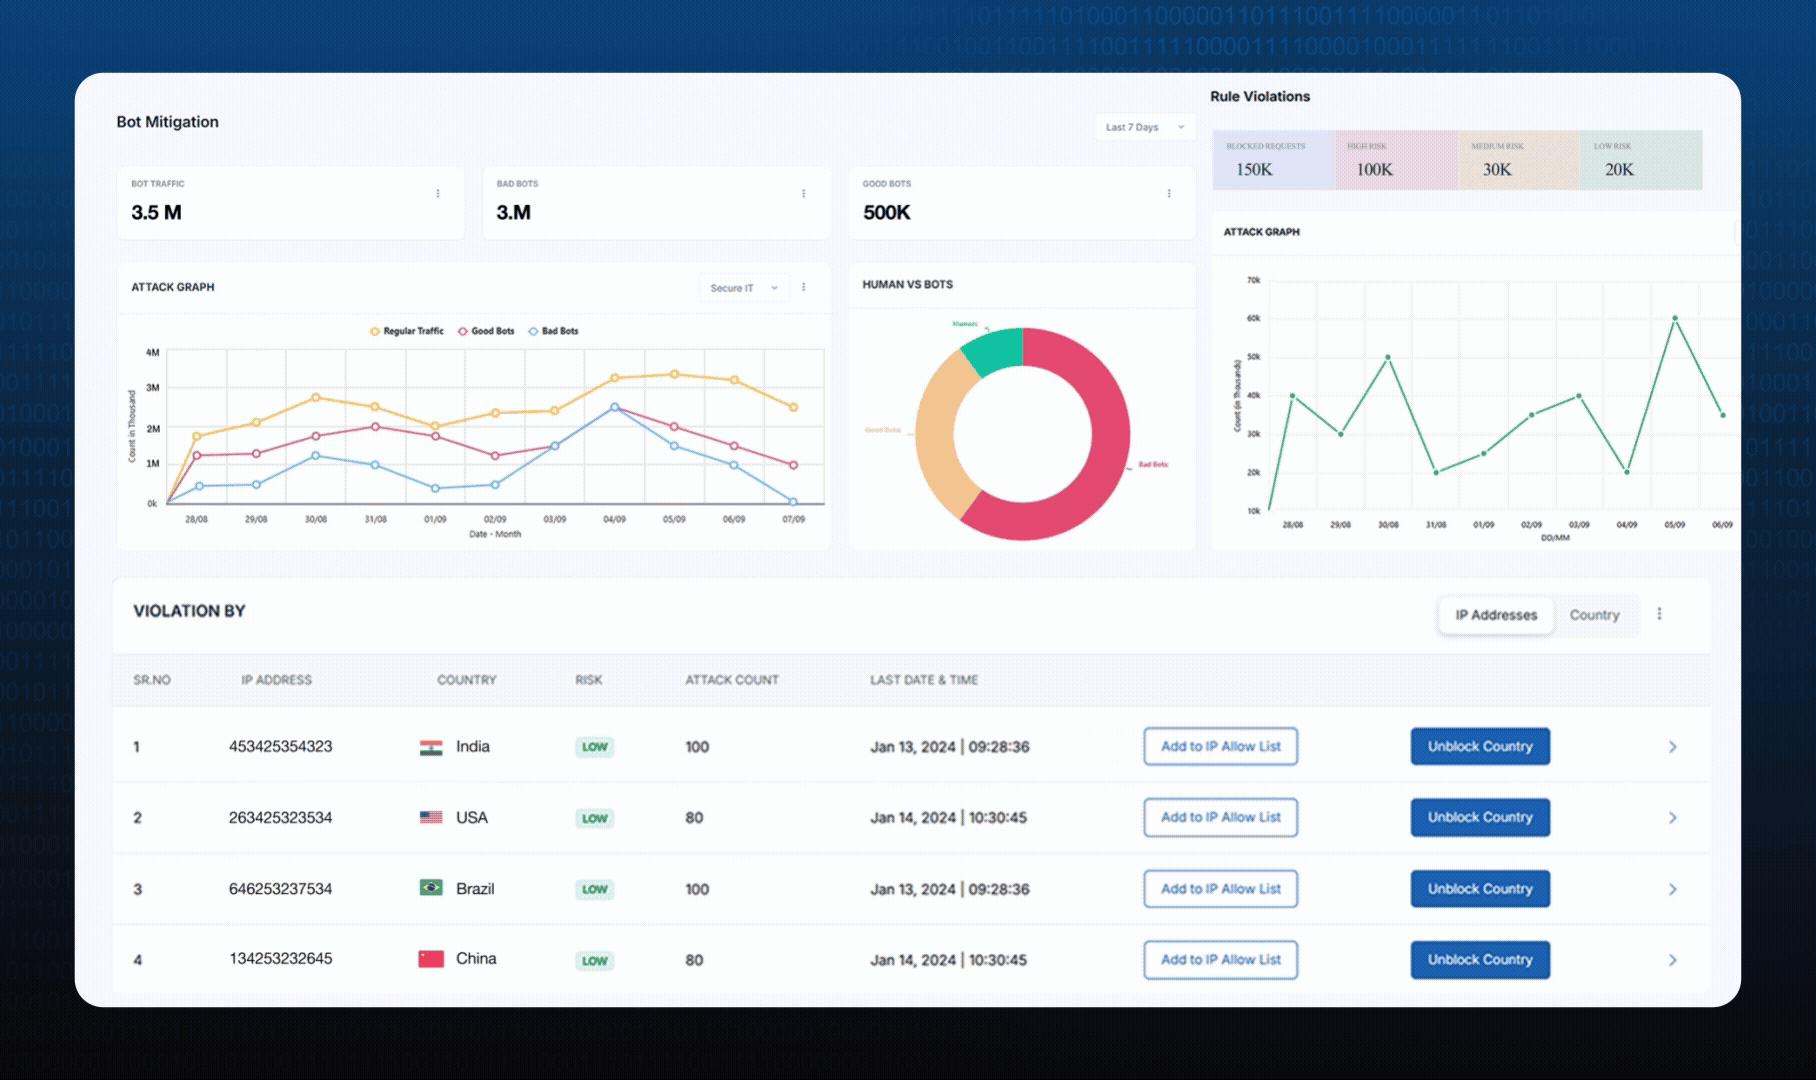
WAF Alerts Hard to Parse, Prophaze Puts It All in One Dashboard

Security and DevSecOps teams get a single, live pane of glass across all apps, with real-time threat maps, risk scoring, and policy controls that cut through false positive chaos so you respond faster without tool sprawl.

DASHBOARD phaze 2

Live attack maps by region, endpoint, and attack type

Risk scoring and threat trends at a glance
Centralized policy editor with one-click deploy
Native alerts to SIEM, Slack, PagerDuty, webhooks
Structured forensics logs for instant investigations
Automated compliance reports (SOC 2, PCI-DSS, HIPAA)

Trusted by High-Stakes Web Environments

Prophaze WAF secures business-critical applications for global enterprises, SaaS platforms, healthcare providers, and financial institutions that cannot afford downtime.
Chief Information Officer
IT Services
“We've had a decent experience overall. The product offers a good range of features and has performed reliably in day-to-day operations.”
Manager
IT Security and Risk Management - Energy and Utilities
“The overall experience was impressive because of the seamless deployment, real-time protection and excellent support throughout the deployment.”
Head - IT/Deputy Director
IT & Compliant
"We've had a very positive experience with Prophaze. Their cloud WAAP Platform offers excellent protection for both web applications and APIs."
IT Associate
IT Services
"Overall, I had a good experience. The process was smooth. I appreciated the timely support and responsiveness of the team."

WAF Security Platform FAQs

Weigh deployment model fit (cloud, hybrid, on-premises, or Kubernetes-native), how the vendor documents its false positive rate, which compliance certifications it names (such as SOC 2, PCI-DSS, or HIPAA), and what support it offers, before comparing price alone.
Ask for a written uptime guarantee and a stated detection-response time, rather than accepting a general “real-time protection” claim. Compare the exact wording of the SLA, including what happens if it is breached.
Enterprise WAF pricing typically scales by traffic volume, application count, or a flat per-application rate. Most vendors require a custom quote once your compliance and support requirements are factored in.
Common options are cloud WAF for public-cloud workloads, hybrid WAF for combined on-prem and cloud environments, on-premises WAF for regulated or data-residency-restricted environments, and Kubernetes-native WAF for containerized architectures.
Run the new WAF in monitoring-only mode alongside the existing one, compare how each handles real traffic, then cut over via DNS or load-balancer routing during a planned, low-traffic window.
Native alerting into your SIEM and incident-response tools, and a way to manage policy through your existing CI/CD pipeline, so security keeps pace with how your team already ships code.
Compare the fully loaded cost of the point tools a unified WAF platform replaces against its own cost, then add the value of reduced incident response time and avoided compliance-failure risk.

Secure Your Web Applications with Prophaze WAF

Scroll to Top
Popup Webinar Image

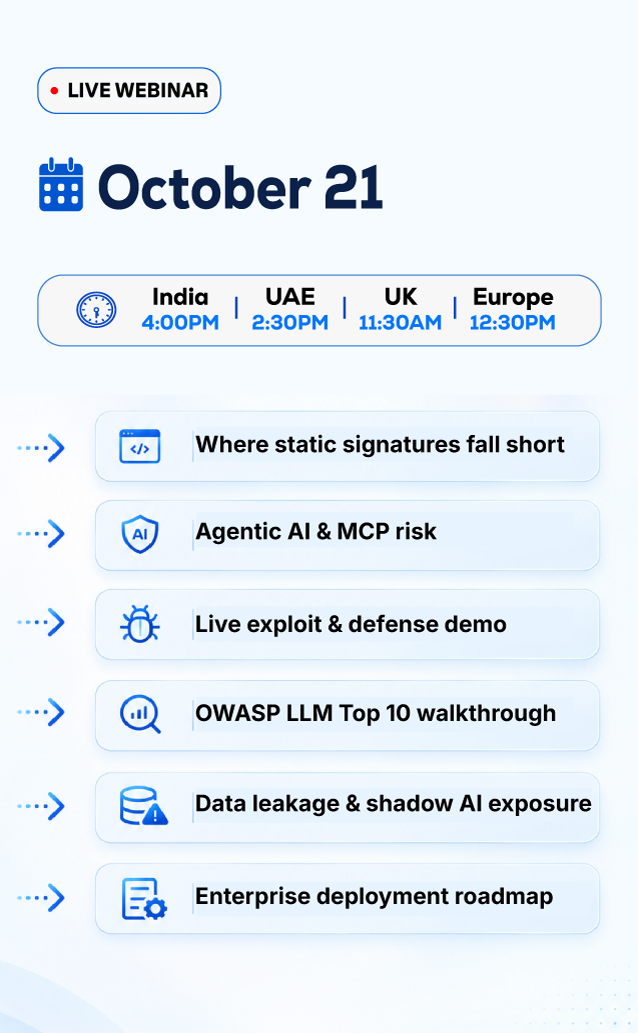
FREE WEBINAR

AI-Native Firewalling: Real-Time Defense for LLM & Agentic Applications

Get practical insights into protecting LLM and agentic applications from emerging attacks before they become your next security incident.