APIs Under Attack, Prophaze's API Security Platform Secures Every Calll
Discover every API, block zero‑day attacks and bots, and enforce policies at scale without slowing your developers down.
- Auto API Discovery & Inventory
- AI-Powered Runtime Protection
- Shadow & Undocumented API Detection
- REST, GraphQL, gRPC & AI/LLM Coverage
- API bot mitigation & Abuse defence
Hidden and Shadow APIs, Prophaze Discovers and Scores the Risk
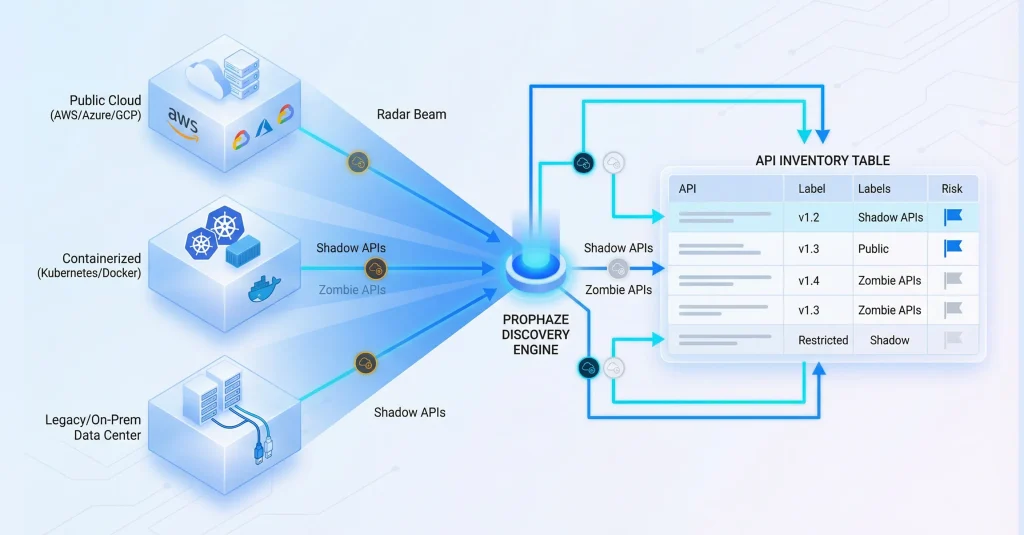
Auto discovers APIs across cloud, Kubernetes, containers, and legacy infrastructure, powering true shadow API detection
Monitors schema, versions, and access controls to detect drift and misconfigurations (API schema validation)
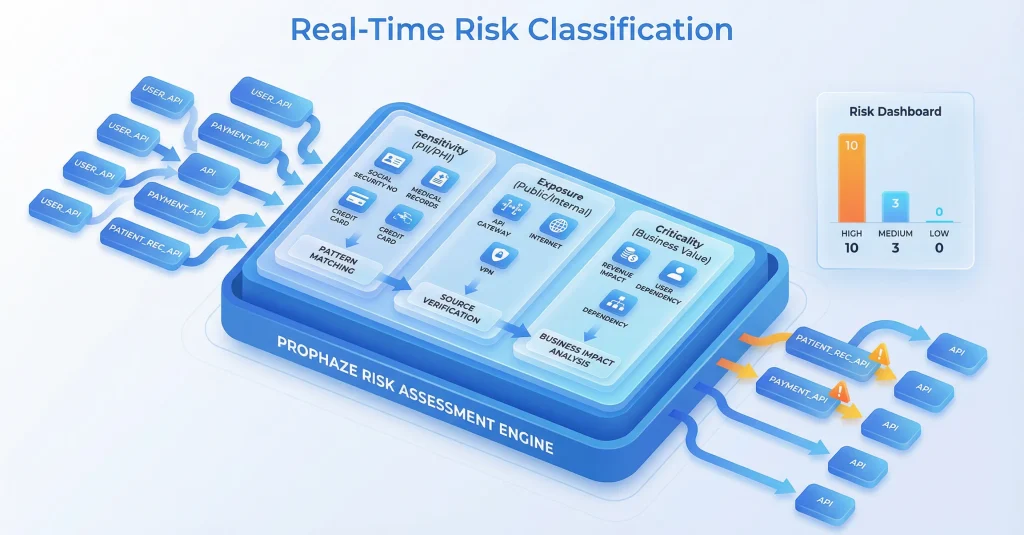
Highlight exposed, non-compliant, and higher-risk endpoints
Classifies zombie APIs, orphan APIs, and undocumented endpoints by exposure and sensitivity
Rising API Threats, Prophaze Delivers Unified Protection

AI-powered threat detection adapts to new attack patterns in real time.

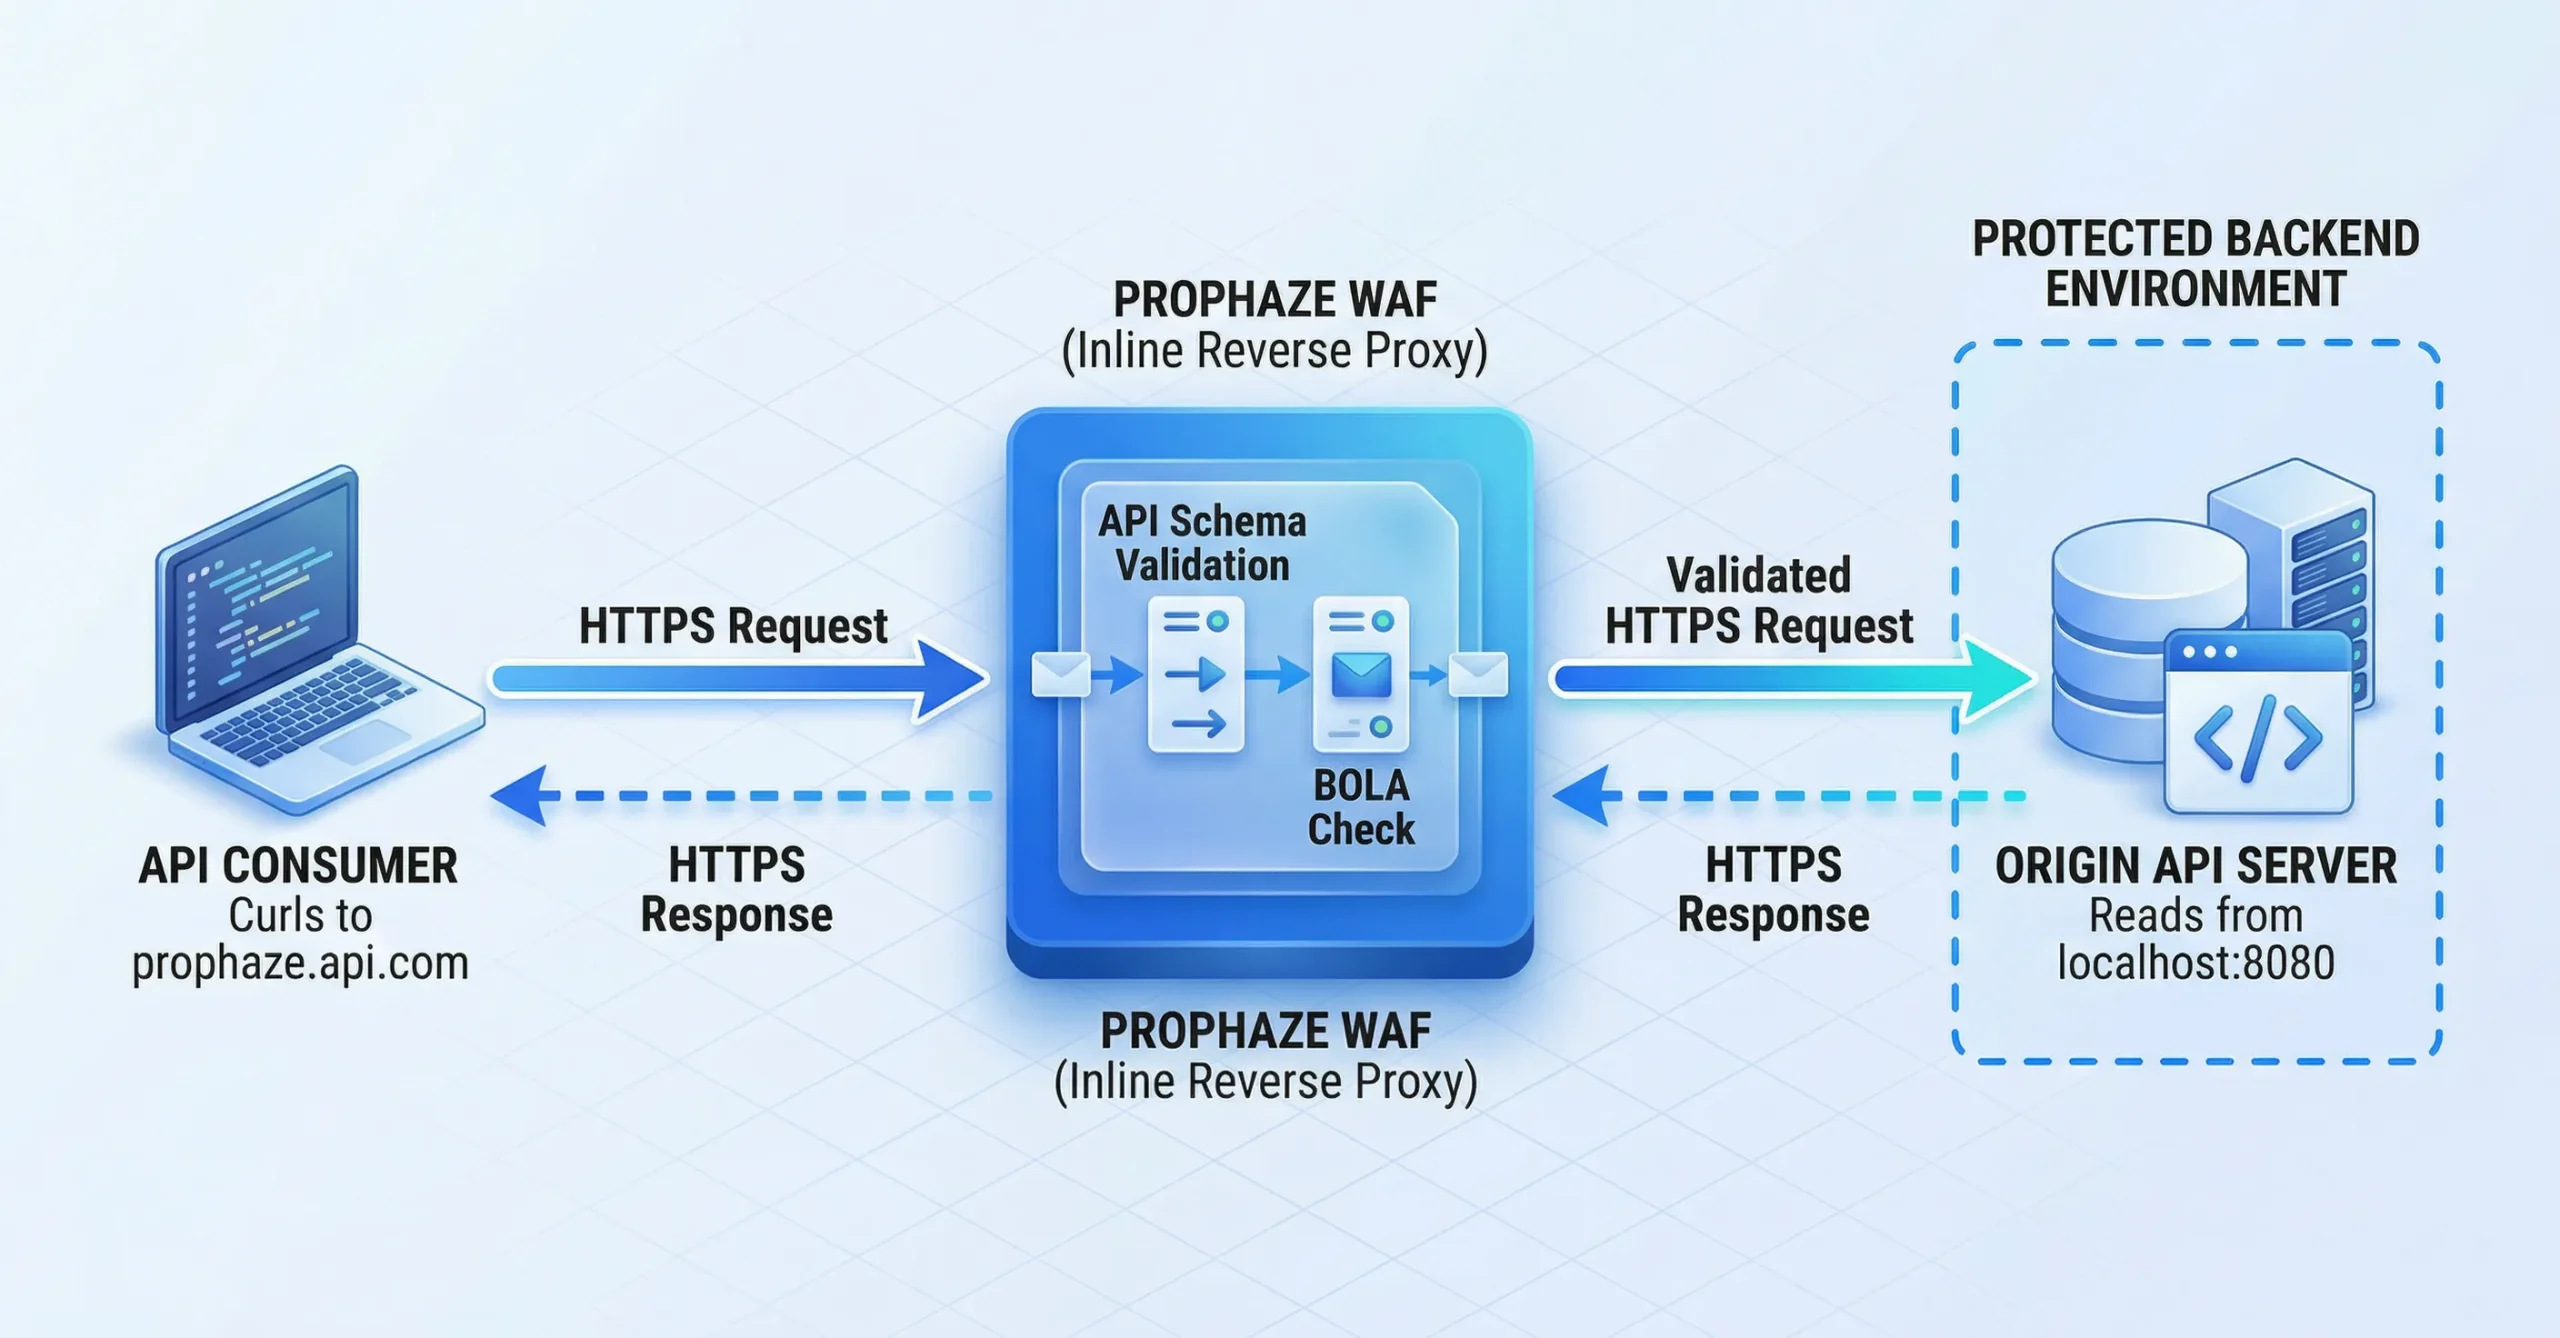
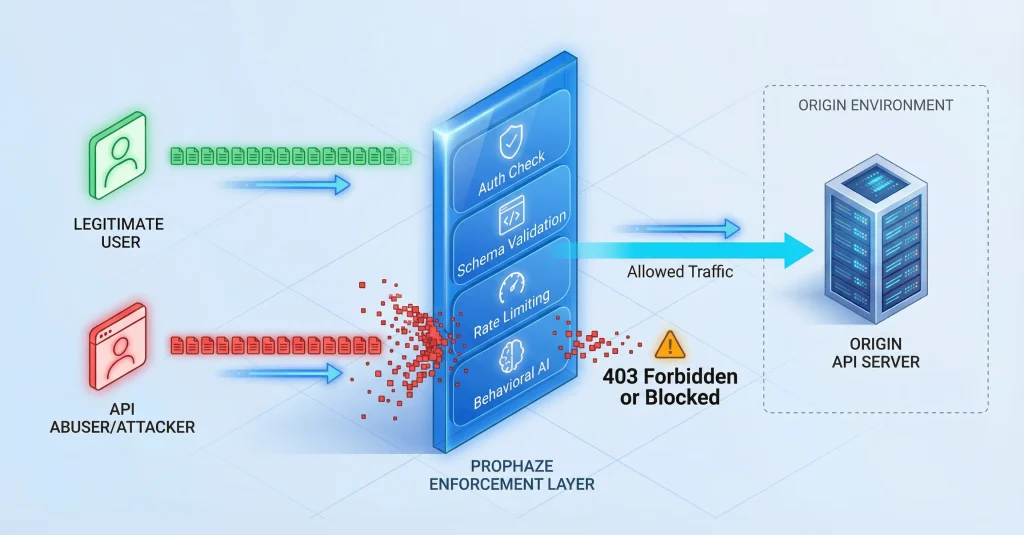
Schema validation and control for JSON/XML, RBAC, traffic quotas, and granular enforcement.

Shadow API discovery surfaces undocumented and legacy endpoints.
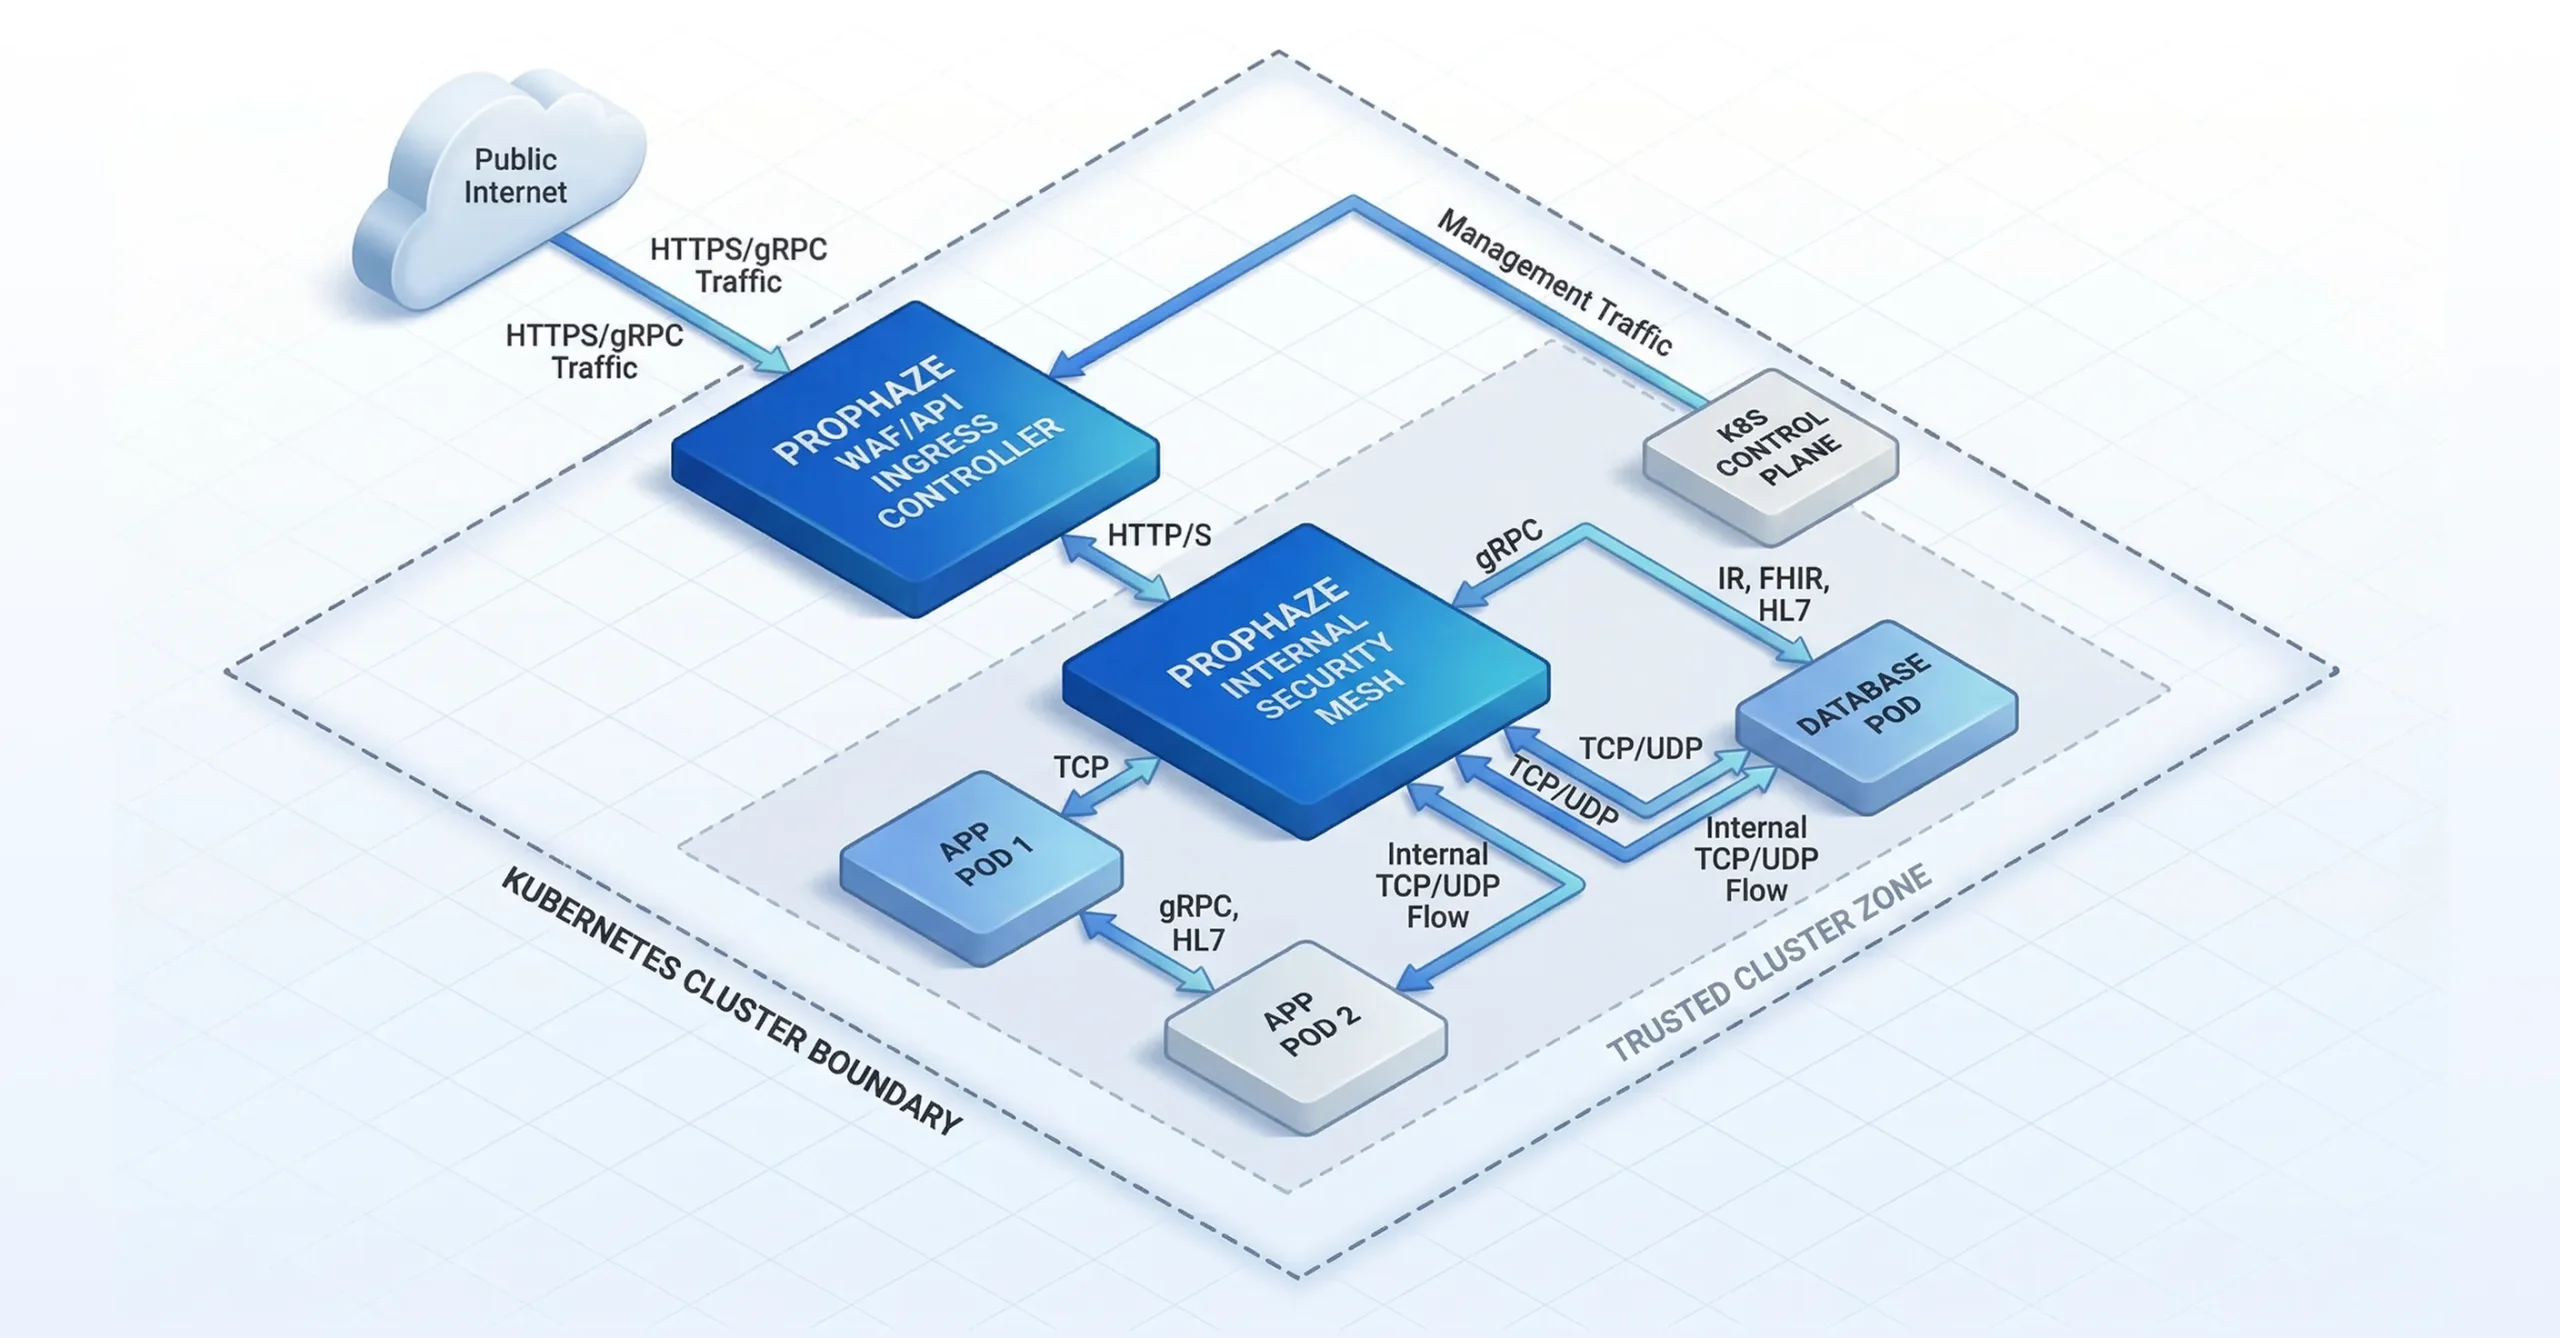
Kubernetes-native security protects both east-west and north-south traffic.

Compliance-ready policies aligned with PCI DSS, DPDP, and other regulatory standards.

Dedicated API Security module with its own dashboard and policy engine.
Continuous OWASP API Top 10 risk scoring as APIs change.
How Prophaze's Runtime API Protection Works, Call by Call
Traffic Ingestion
No need for SDKs or code changes. Captures API calls at the edge.
Behavioral Analysis
Analyzes API usage patterns and evaluates new requests against established behavioral baselines.
Real-Time Mitigation
Blocks or challenges suspicious requests without disrupting genuine users.
Prophaze
API Security Cycle
Deep Payload Inspection
Examines API requests and responses to identify malicious payloads, protocol violations, and suspicious content.
Anomaly Detection
Instantly, AI flags unusual payloads, data structures, or frequencies.
Continuous Learning
AI models progress in response to emerging traffic patterns and evolving attack vectors.
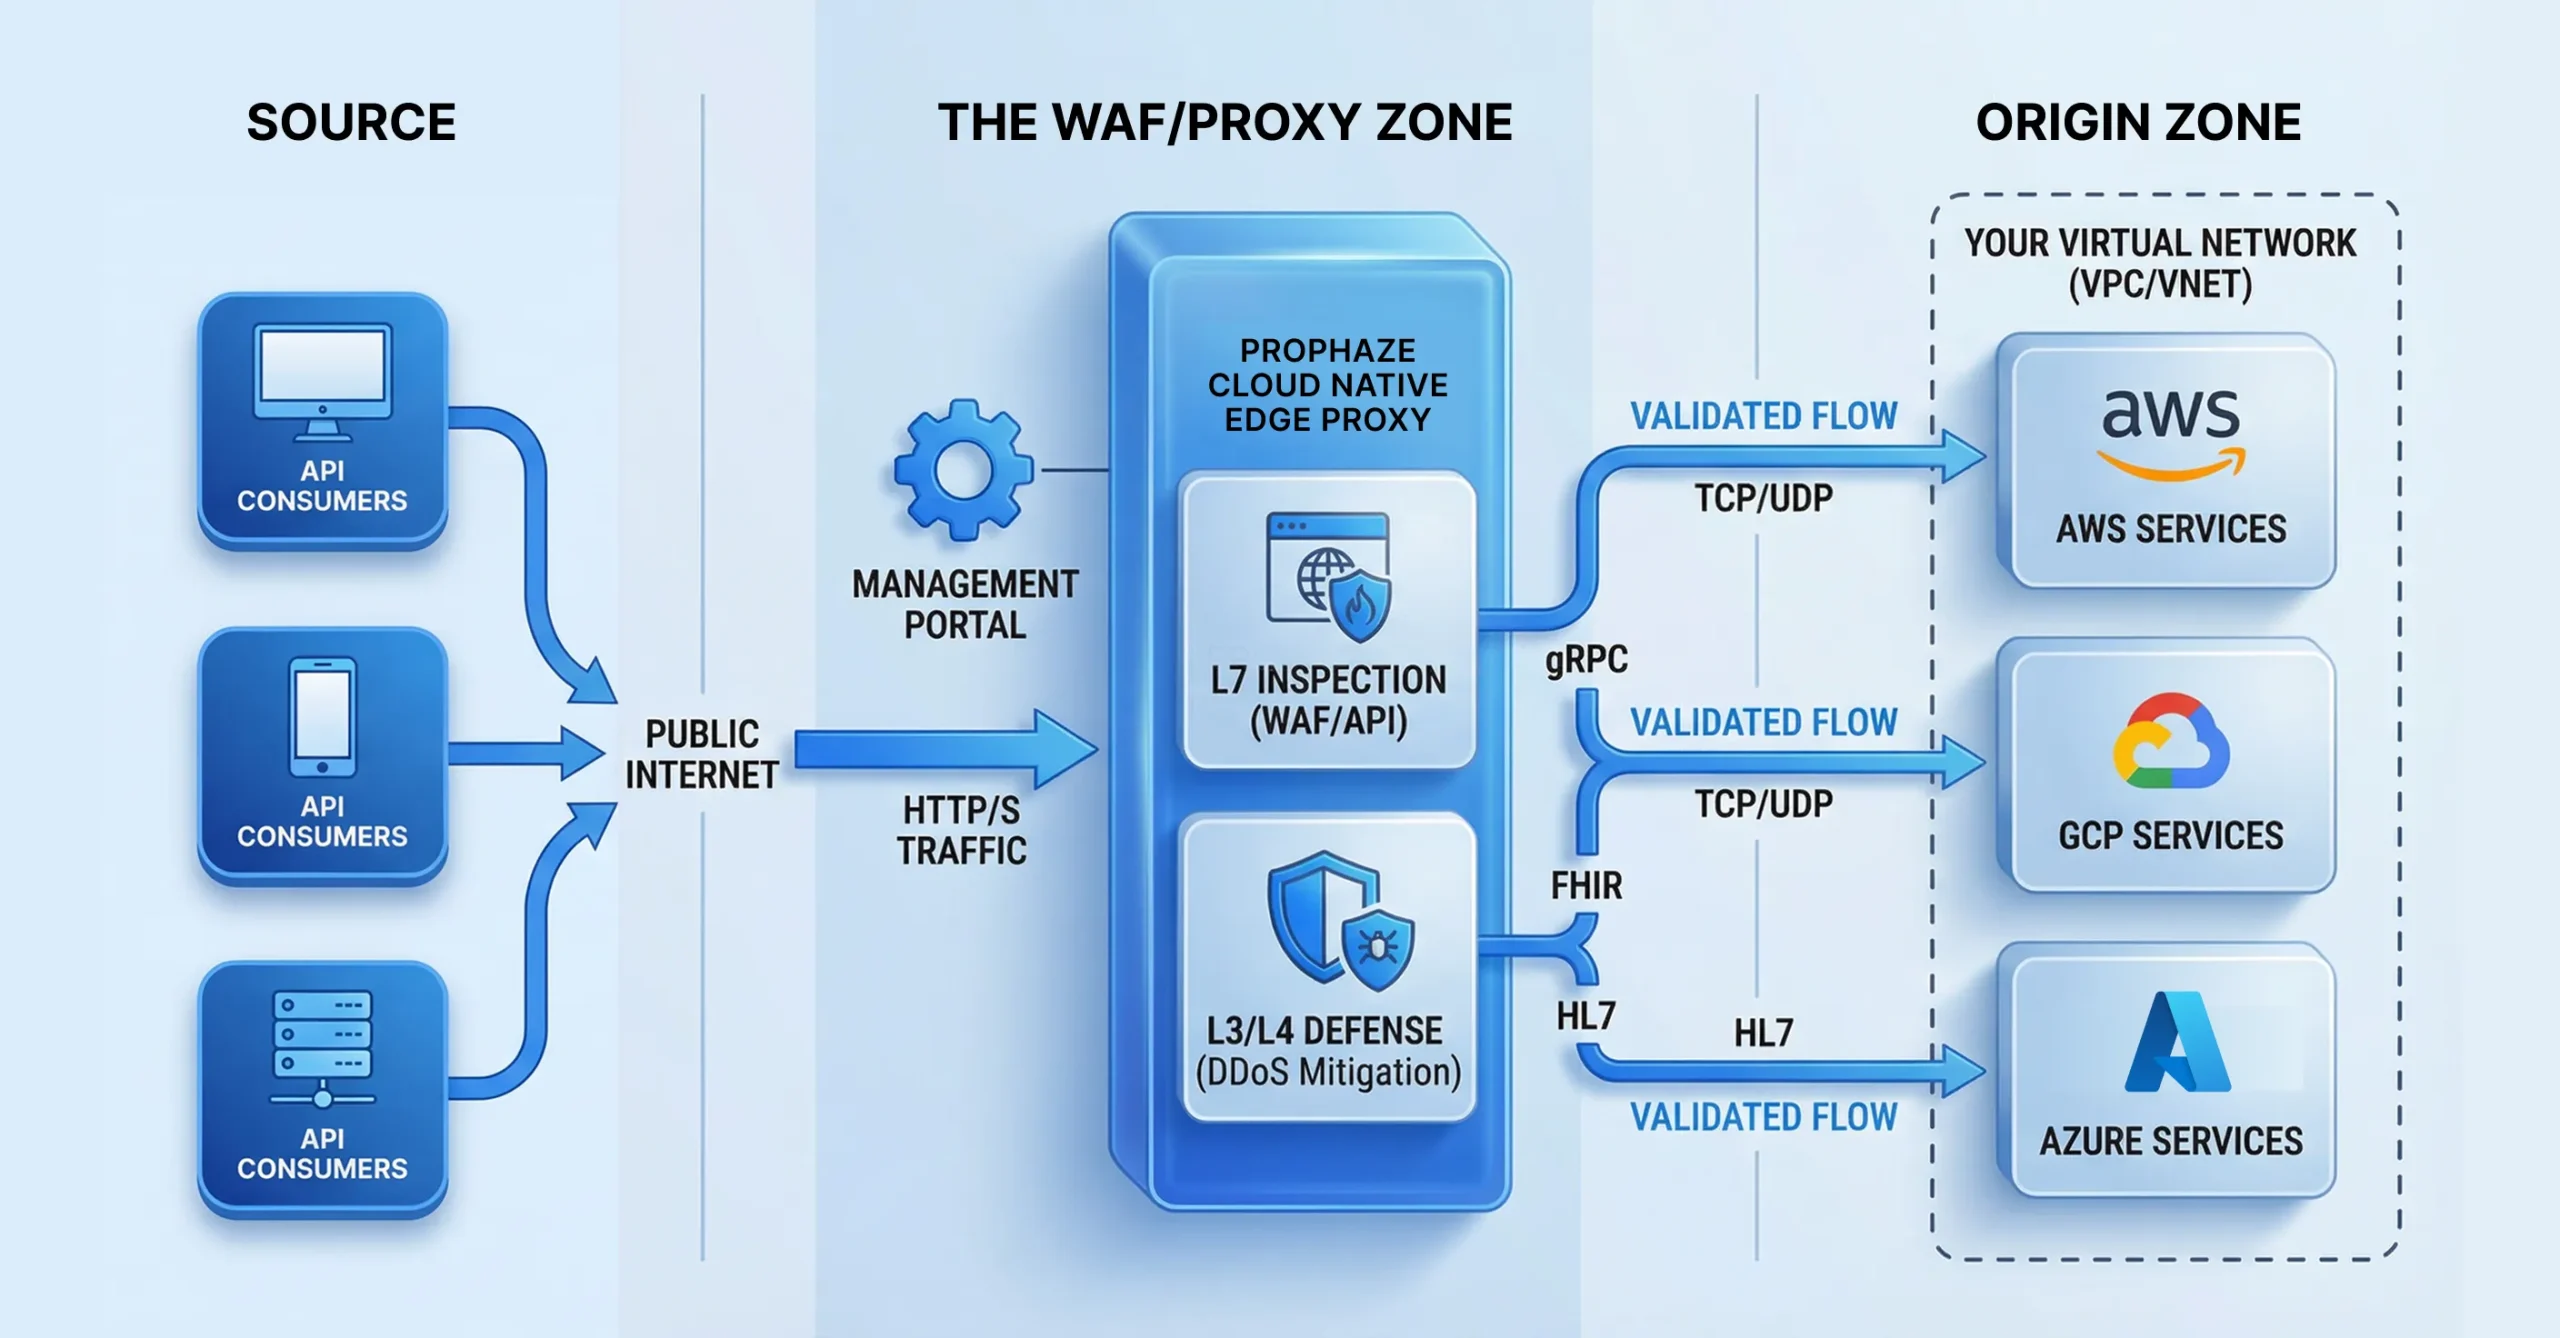
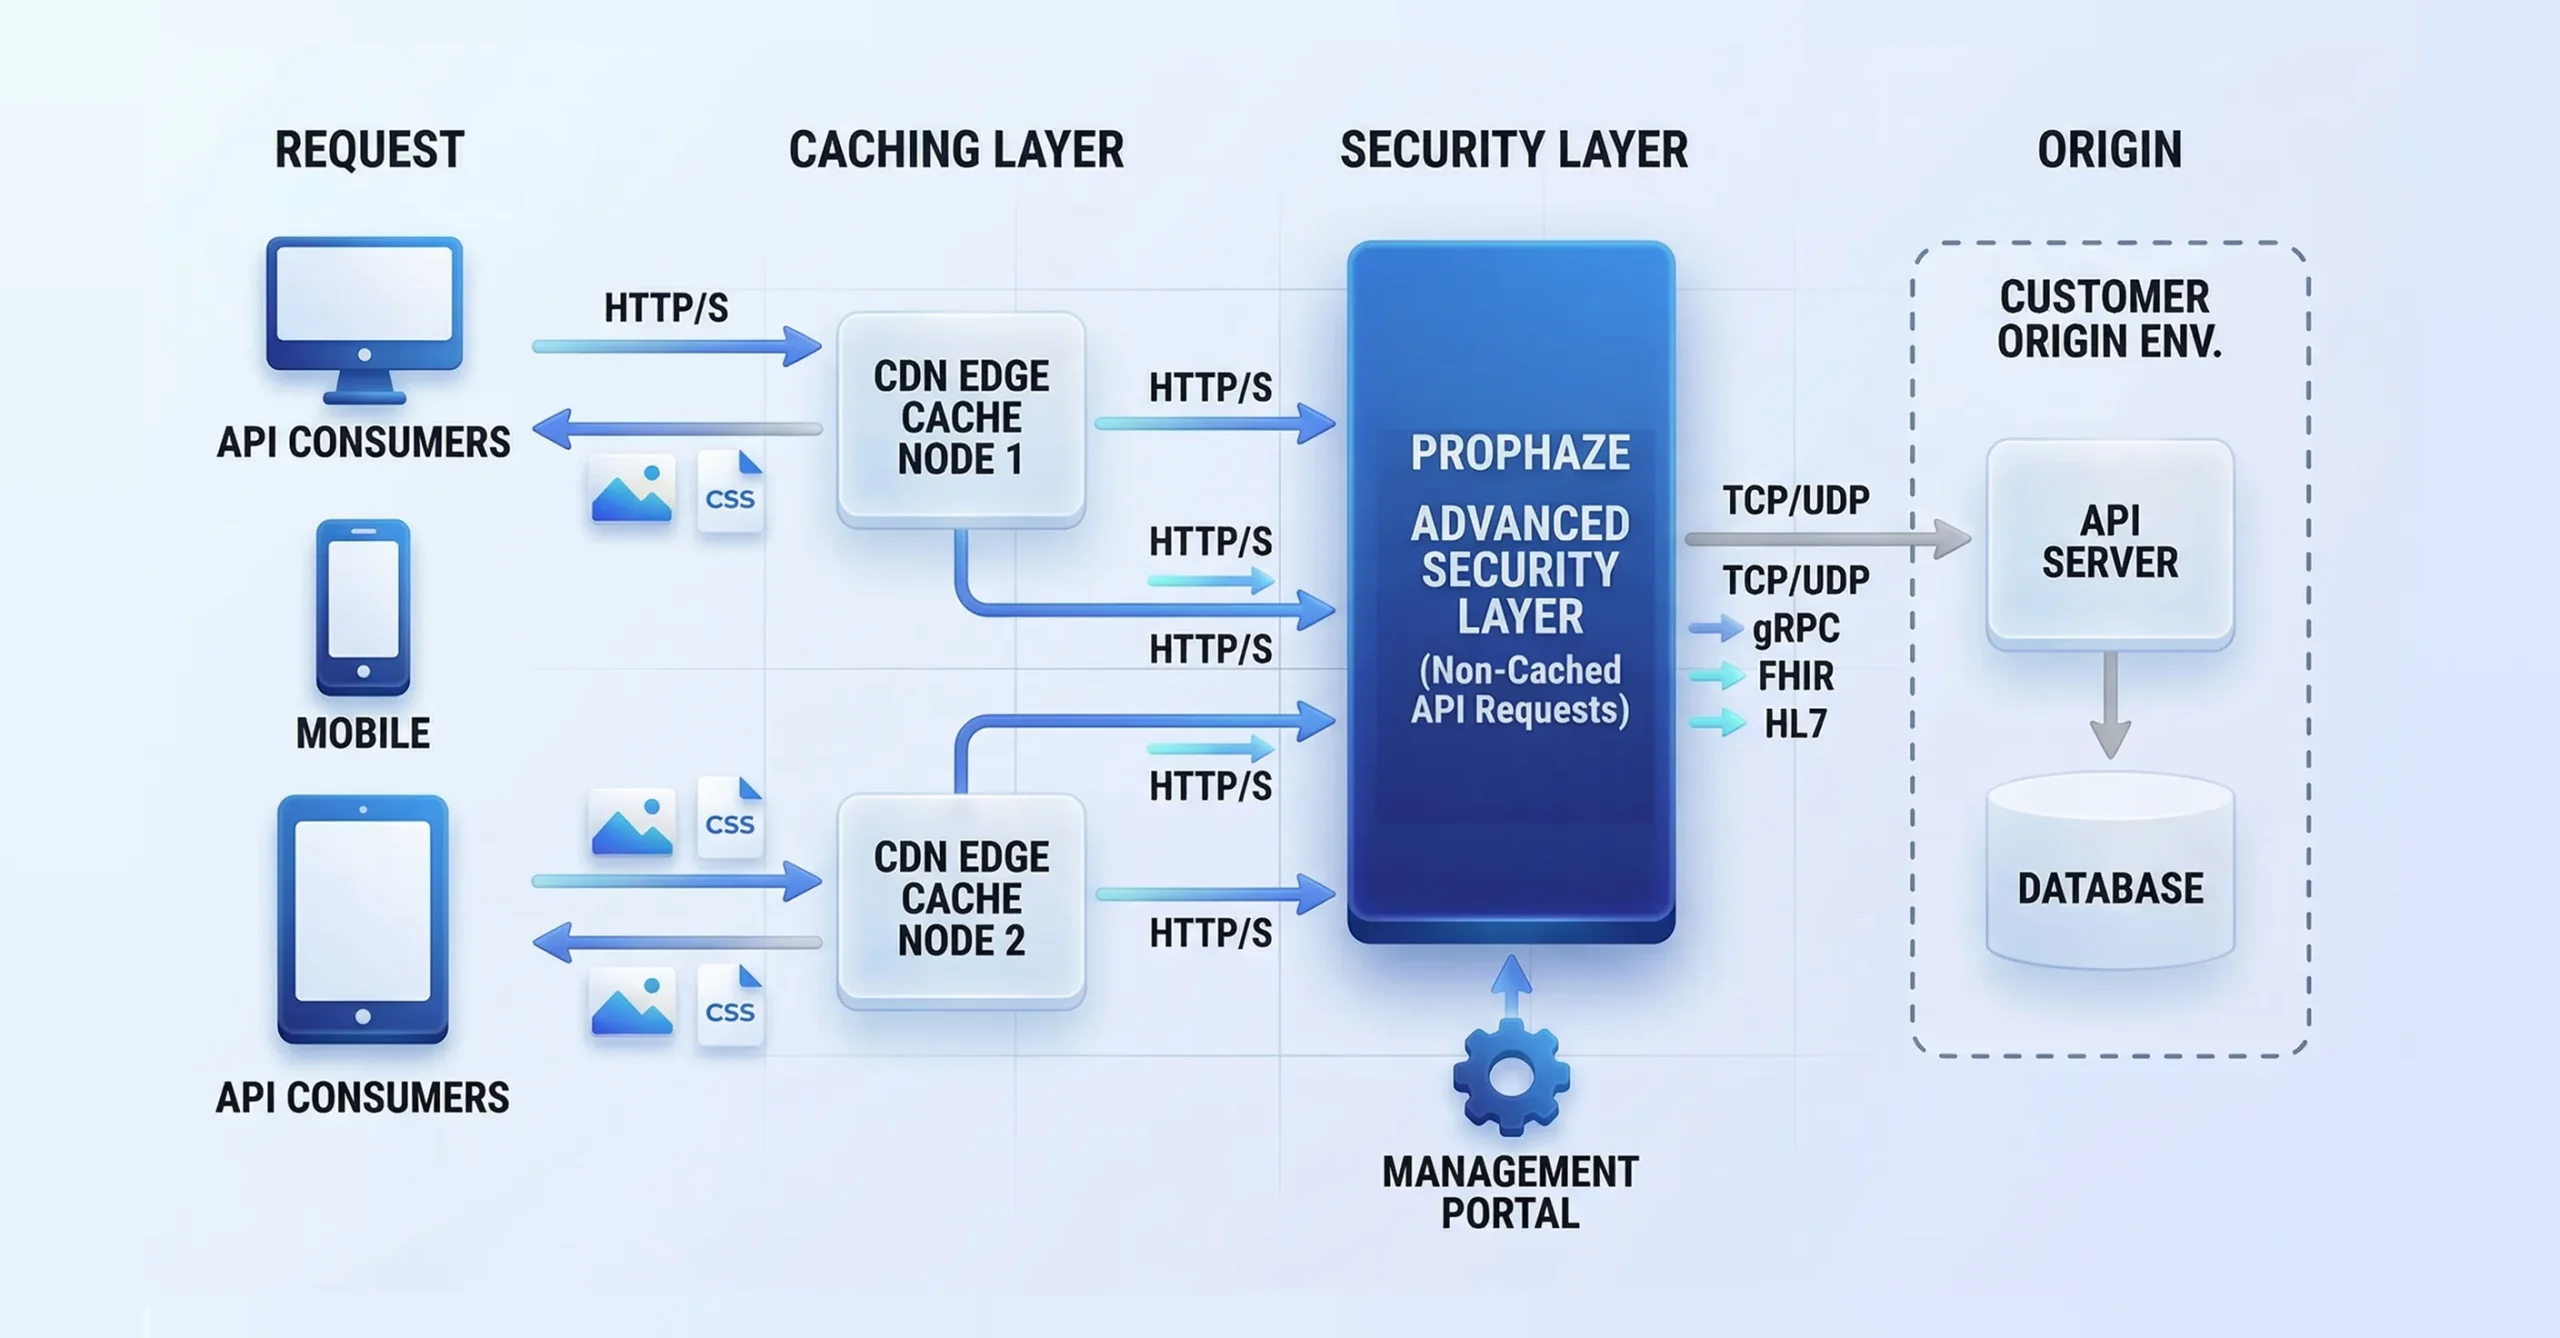
Deployment That Fits, Your Architecture
Blind API Sprawl Turned into a Fully Secured Estate in Three Moves
Discover and classify every API
- Auto-discover known, unknown, and shadow APIs across cloud, containers, and legacy environments.
- Continuously track inventory, schema, versions, and access levels.
Assess and Prioritize API Risk
- Identify exposed, misconfigured, vulnerable, or high-risk APIs and prioritize remediation based on API sensitivity, behavior, and threat context.
- Continuously update risk as API traffic and configurations change.
Protect and Govern Every API
- Apply API-specific policies, OWASP API Top 10 controls, authentication and authorization protections, rate limits, and granular enforcement.
- Monitor API security posture continuously and maintain audit-ready visibility across the API estate.
- Manufacturing
- Layer 7
Busy DevSecOps Teams, Prophaze Automates API Security in the Pipeline

No SDKs or code rewrites needed
CI/CD API security integration with API Security as Code
Works with REST, gRPC, GraphQL, and OpenAPI specs
RBAC enforcement API and full audit trails
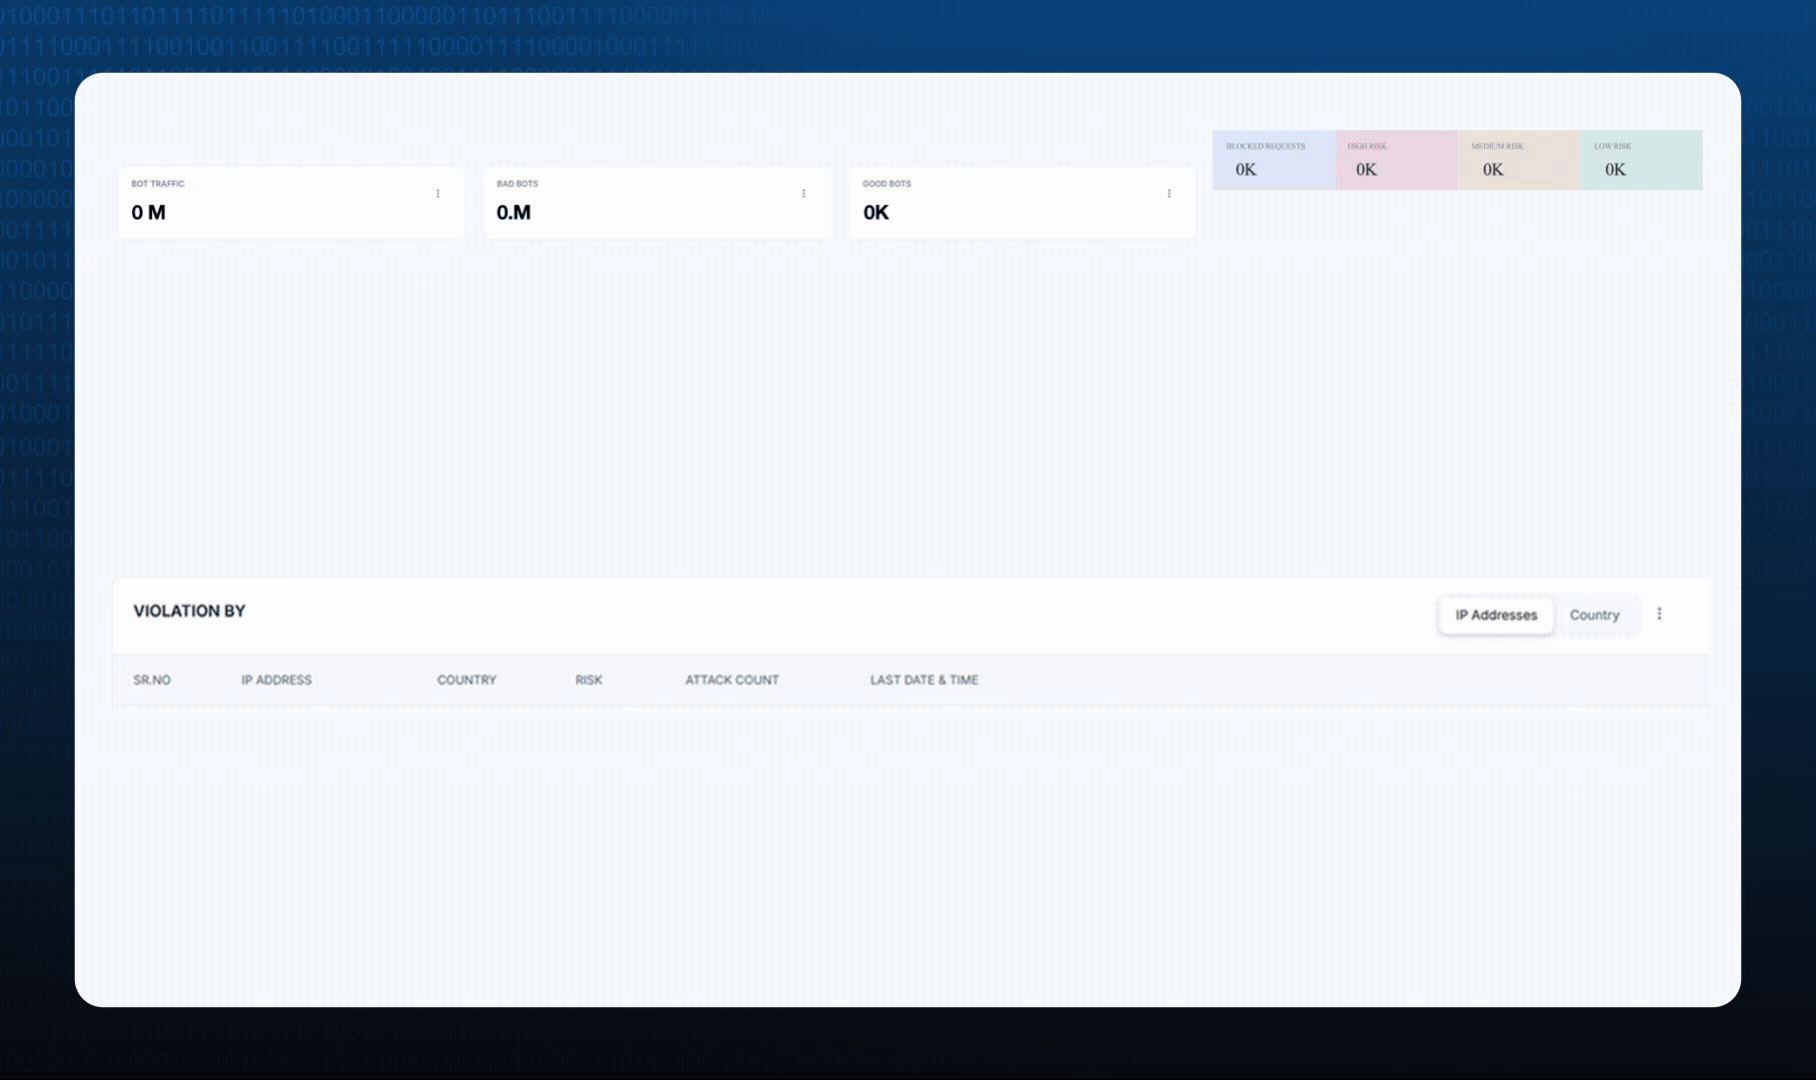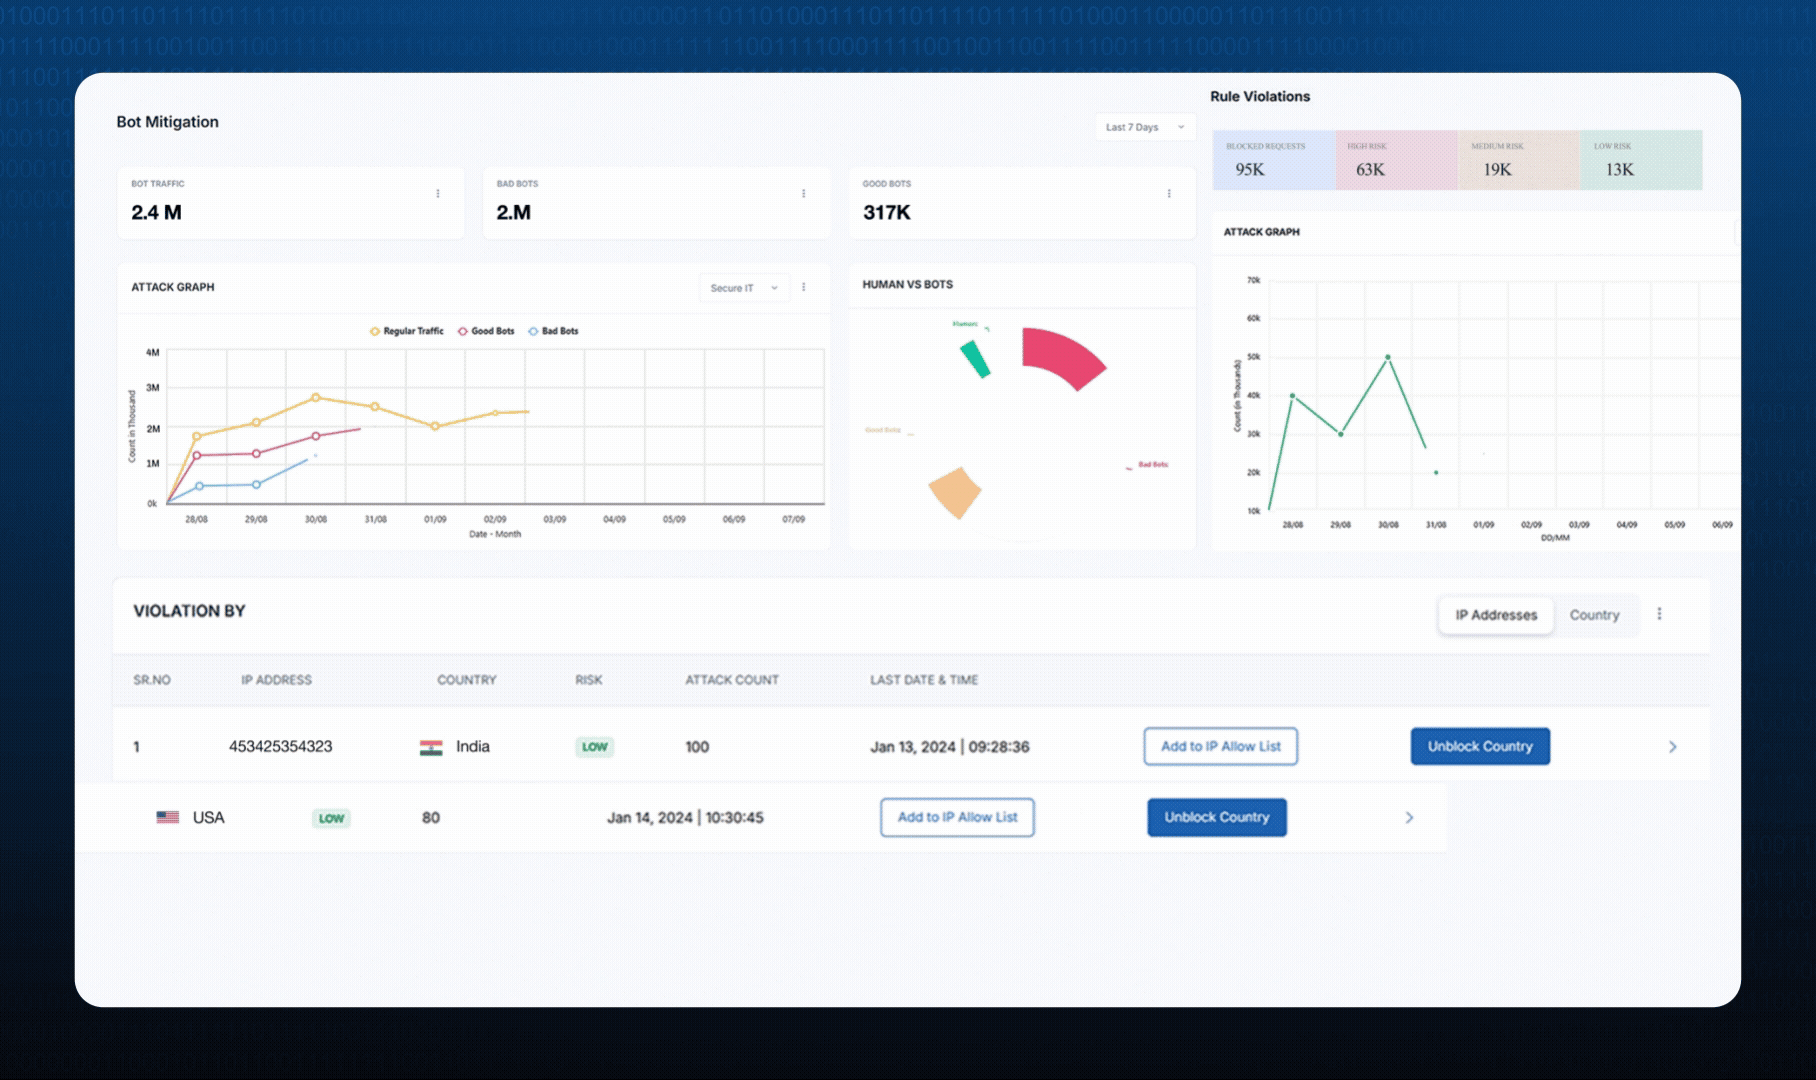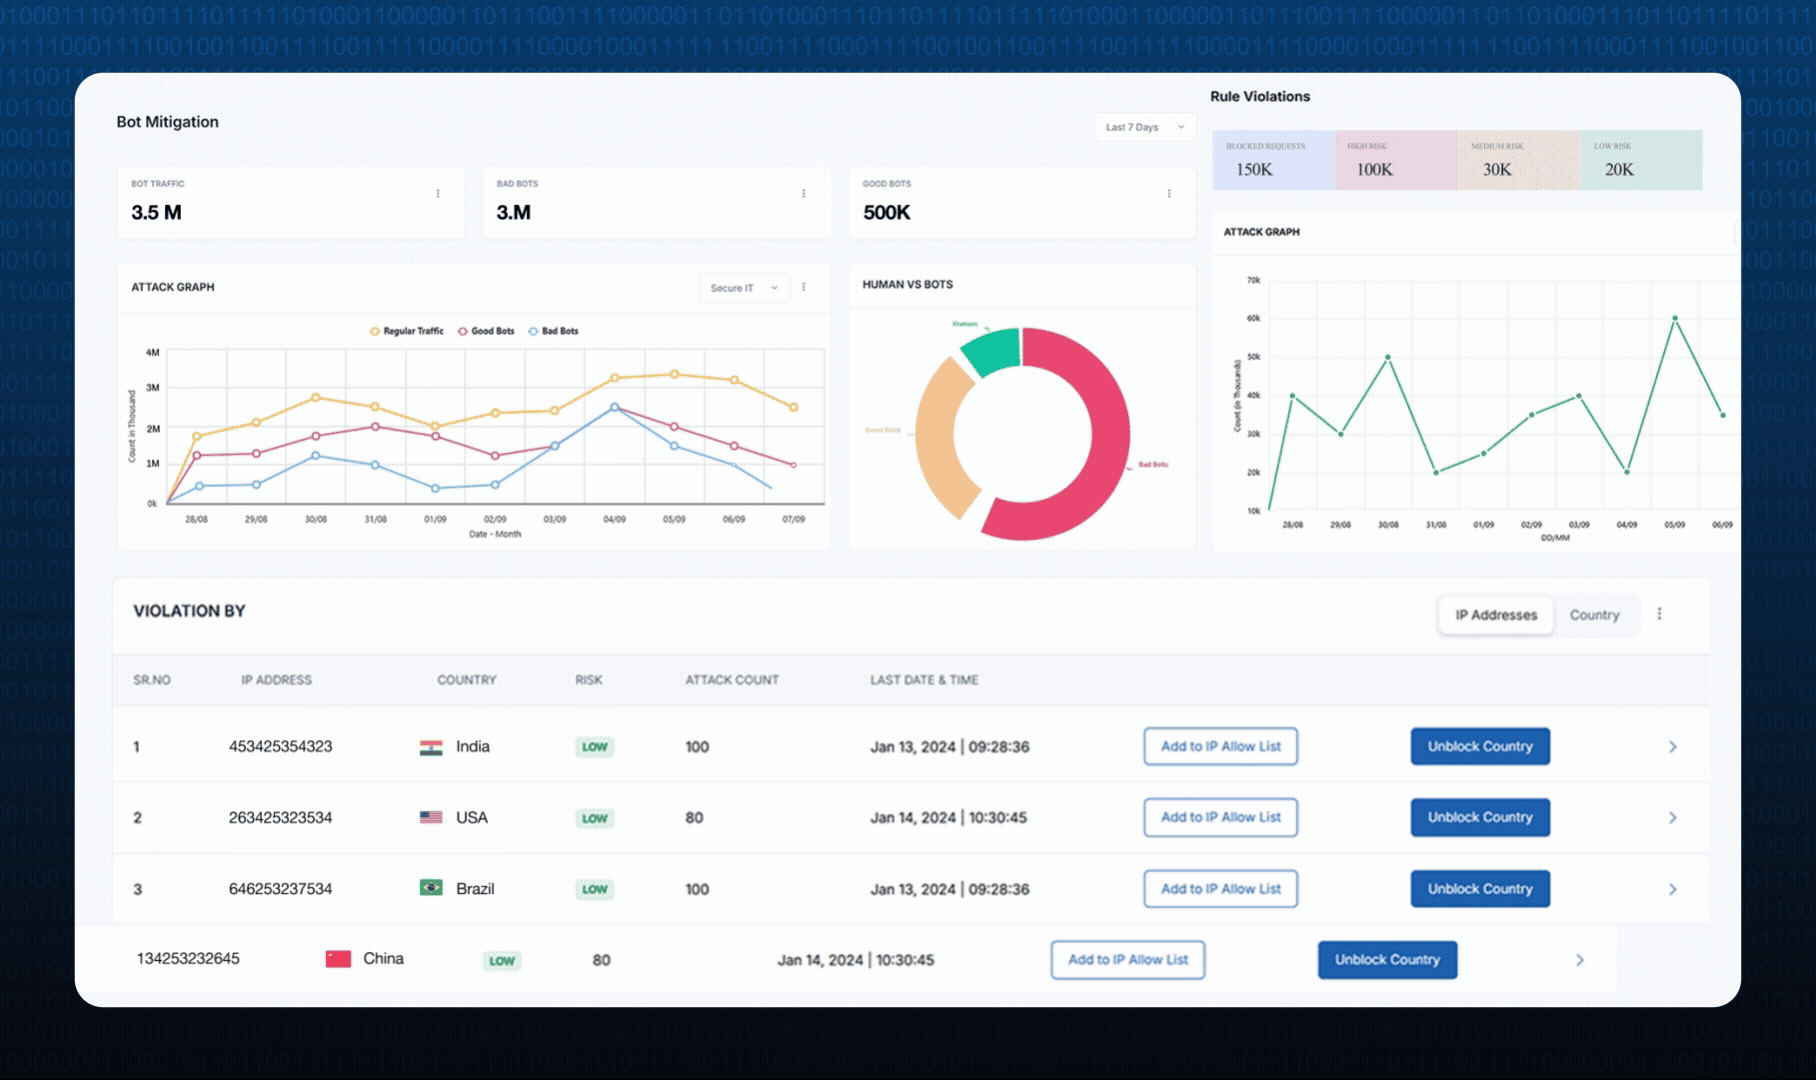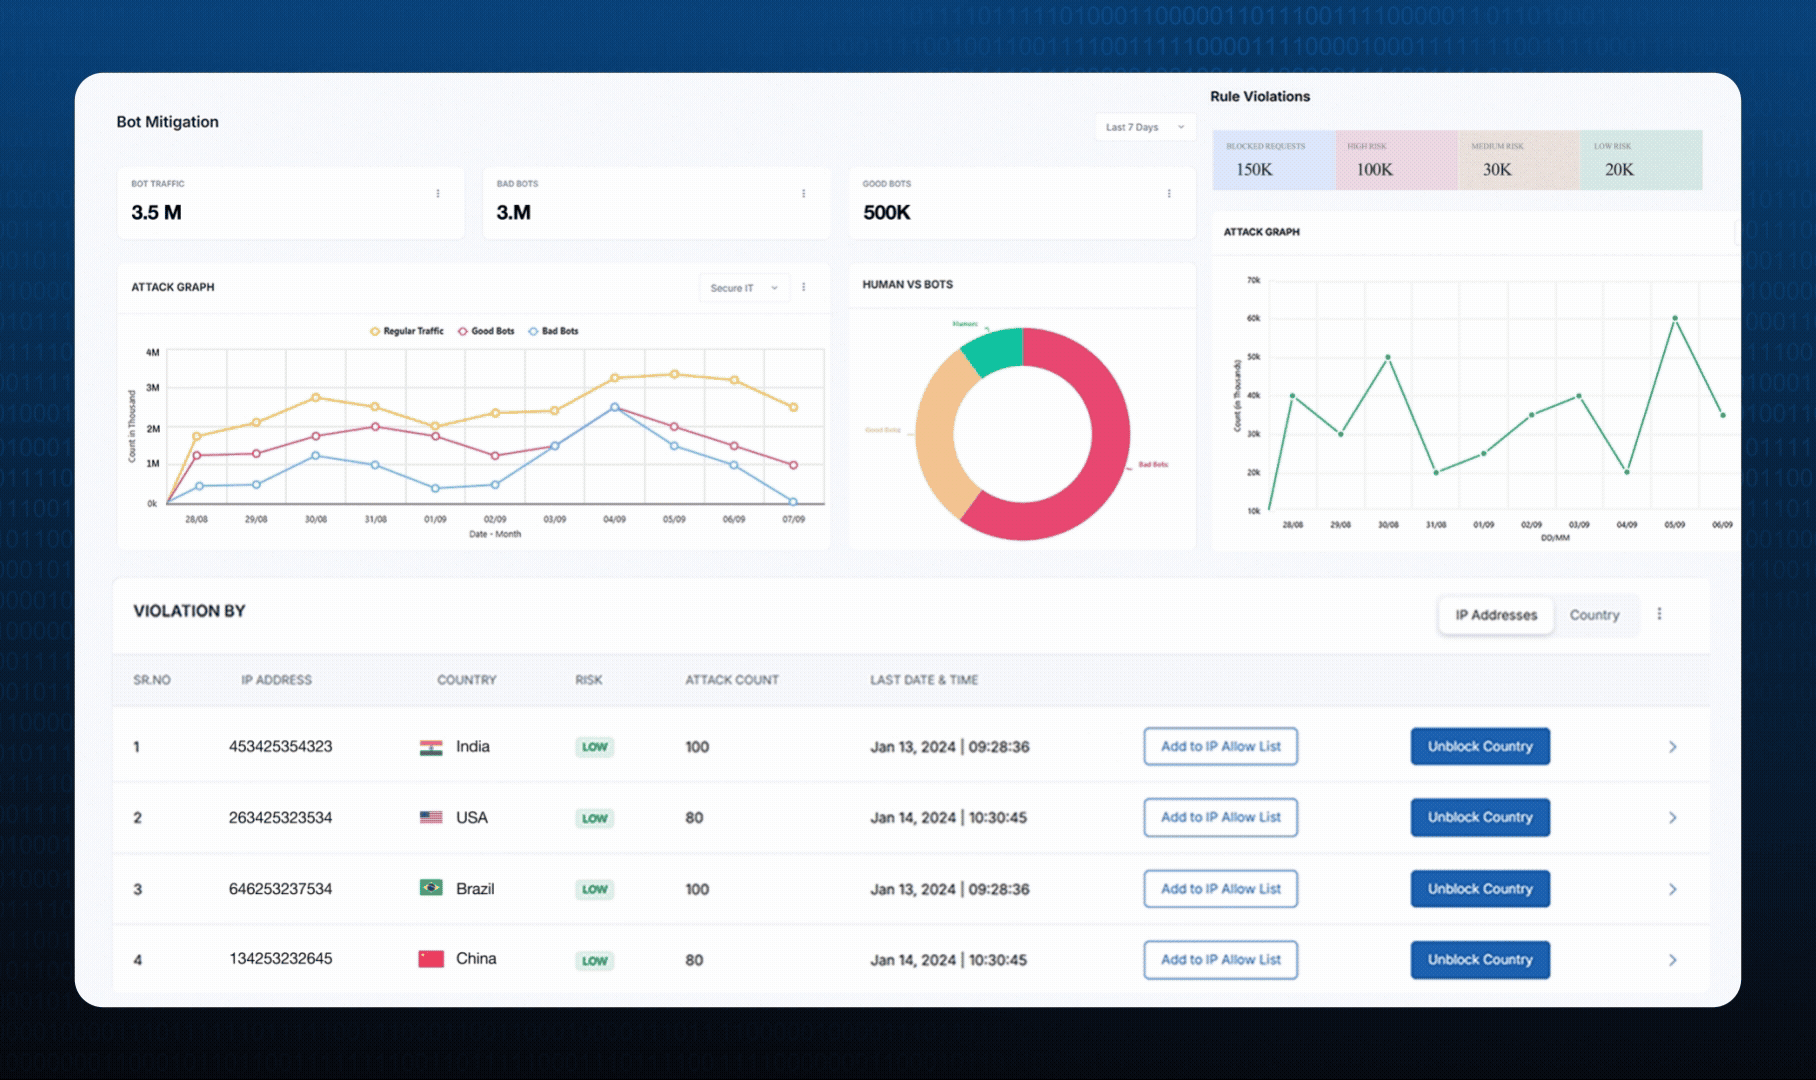
One Console for Every API, Every Team
Trusted by High-Stakes Environments
Prophaze secures APIs for critical infrastructure, global SaaS platforms, healthcare providers, and fintech leaders that cannot afford downtime or data leaks. Security teams rely on Prophaze to reduce risk quickly without adding operational complexity.
API Security Platform FAQs
What should I look for in an API security platform?
How much does an API security platform cost?
What is the best API security platform for enterprises?
What is the ROI of an API security platform?
Which API security vendor offers PCI DSS and HIPAA compliance support?
How do I migrate to a new API security platform without downtime?
Protect Your APIs from Modern Threats
- Secure all API traffic, block abusive bots and zero-day attacks, and get real-time threat insights without slowing delivery.